Replacing TMG with IIS ARR for an Exchange Hybrid

On September 12th 2012 Microsoft announced that the TMG Forefront 2010 product will be discontinued. Microsoft obviously had to replace this product with alternatives. 
One of those products is the Web Application Proxy feature in Microsoft Windows Server 2012 R2   Web Application Proxy Deployment Guide 
Another product which was was released was Microsoft Application Request Routing 3.0 
This product plugs into IIS and can act as a reverse proxy to publish Exchange 2013/2010.
The Exchange Team Blog have a three part article on how to set it up and install it
Part 1 , Part 2 , Part 3 

There is an excellent Article on the Office365 community site on how to configure TMG 2010 for an Exchange Hybrid scenario.

And the key paths that require publication from the Hybrid Server are 
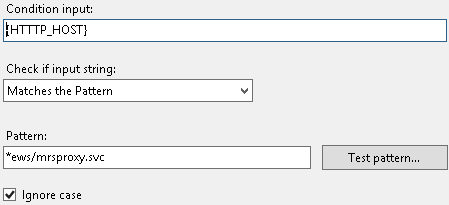
  • /ews/mrsproxy.svc
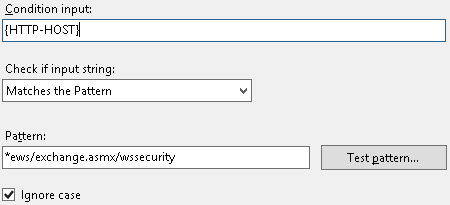
  • /ews/exchange.asmx/wssecurity
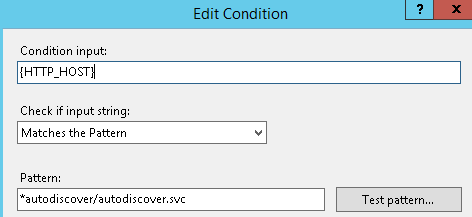
  • /autodiscover/autodiscover.svc/wssecurity
  • /autodiscover/autodiscover.svc
So how do we get these paths working in IIS ARR?????

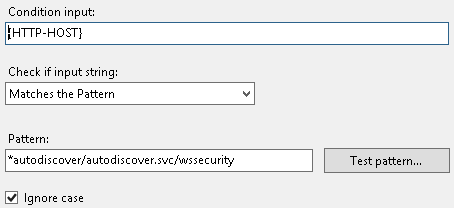
The following 4 images are how we add the paths into the https url re-write section of IIS ARR


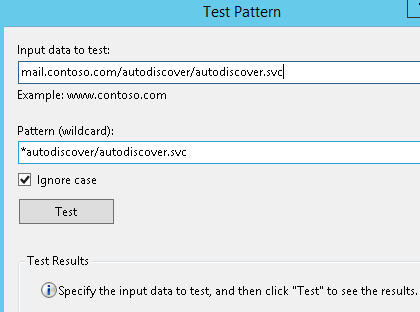
And then finally to test the path you enter the public url as per the image above mail.contoso.com/autodiscover/autodiscover.svc and when we press test.
GREEN LIGHTS APPEAR 🙂 

The main purpose of this blog was to help people understand how to get different path types into IIS ARR as it took me a bit of time to configure. A server 2012 R2 server can be provisioned in minutes in the right environment. Publishing Exchange Hybrid services like this from a DMZ is in line with Microsoft Best Practices.

Exchange Hybrid Mailbox Migrations slow when using TMG

When using Exchange online in Hybrid mode , if you want to have a unified global address list with exchange online users and onpremise users then you need to create on premise blank mailboxes for the users that you want to use exchange online and then create ‘remote move requests‘ to move the onpremise mailboxes to exchange online.

During the move request , if you open the log you may see ‘Relinquishing job because the mailbox is locked‘

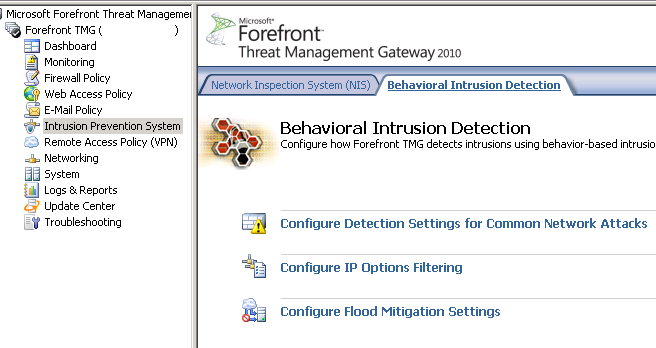
So in order to fix this and really speed up the remote move requests we need to go to the intrusion prevention section of TMG and then the Behavioral Detection\Configure Flood Mitifgation Settings as per the image below.

We click on the link for Configure Flood Mitigation Settings and then click on ‘IP Exceptions‘ and create a new computer set. In the image below I called it ‘Exchange Online Protection‘ and add a computer set with the exchange online protection range as per the image below

All of the Exchange Online Protection IP ranges can be found at this SITE 

You can susbscribe via RSS feed HERE to the Microsoft Online IP Ranges 

So now Remote move requests will migrate a lot quicker 🙂 

Publish CRM2011 IFD via TMG 2010

I recently had to publish Microsoft Dynamics CRM2011 with claims based authentication and internet facing domains.

So to set this up within the lan , HERE is an excellent blog on how to setup the configurations on CRM 2011 and ADFS within your LAN. So the purpose of this blog posting is to show people how to securely publish CRM 2011 via TMG.


In terms of best practice , it is never a good idea to punch a hole through a corporate firewall to a service running on a server on a LAN. I am surprised Microsoft are discontinuing their Forefront TMG Servers on December 15th. Microsoft will continue to support TMG but wont be selling it anymore from December 15th 2012.

TMG 2010 needs to be patched in a certain order.

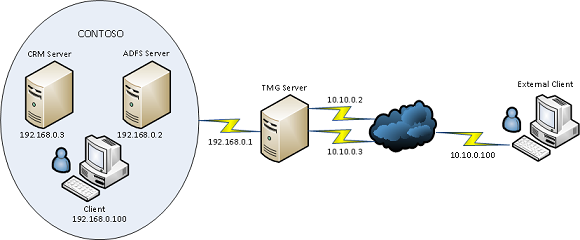
So the image below describes the required topology for CRM 2011 IFD via TMG and I will outline the steps needed to implement this and get it working as there are quite a few things left out of the official Microsoft documentation.


Create WebListener

So as per the image above we would need to add the IP’s 10.10.10.2 & 10.10.0.3 to the external nic on the tmg server.During the creation of the web listener when the external network is created we click the radio button and add the dmz ips we added earlier on as per the image below.


The next section in the web listener creation is very important. Select the SSL Certificate for each of the DMZ ips we added in the previous component of the web listener creation.
Ok so we have the web listener created , now is time to get all the rest of the dependencies in place before we can quickly create the web publishing rules.

Disable ADFS Server Loopback Check
1. Click Start, click Run, type regedit, and then click OK.
2. In Registry Editor, locate and then click the following registry key:HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Lsa
3. Right-click Lsa, point to New, and then click DWORD Value.
4. Type DisableLoopbackCheck, and then press ENTER.
5. Right-click DisableLoopbackCheck, and then click Modify.
6. In the Value data box, type 1, and then click OK.
7. Quit Registry Editor, and then restart your computer.


DMZ to LAN & LAN to DMZ Routing

The next thing to take into account is the routes from the TMG Server to the LAN and from the LAN to the DMZ. In the diagram above it is a very basic small network. But most companies can have multiple subnets.
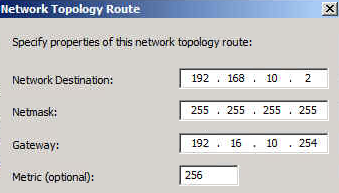
So lets say the the internal adfs server is 192.168.10.2 , To enable TMG to route traffic to this server we would need to add a network routing rule as per the image below.

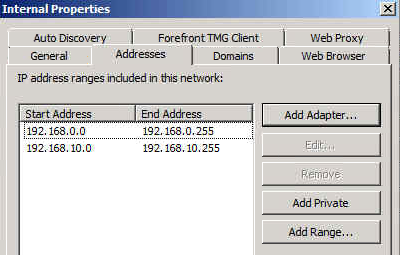
We will also need to add the extra subnet to the internal network as per the image below

Nearly done! We may also need to add a static persistent route to the ADFS & CRM Server so it can then get back to the TMG Server.

External / Internal DNS Records

adfs.contoso.com  points to adfs server

dev.contoso.com points to crm server
auth.contoso.com points to crm server
orgname.contoso.com points to crm server

Creating Web Publishing Rules

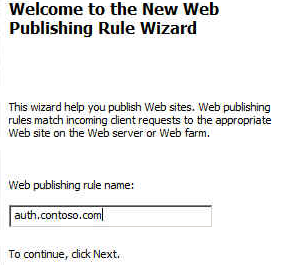
Ok so now we will create one rule for the crm server first.


Publish a Website
Use SSL
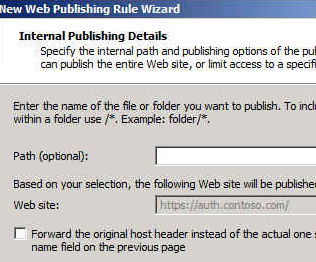
Enter the IP address of the CRM Server
Leave the defaults and click next
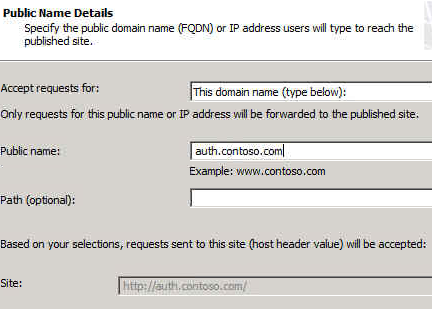
Enter the public name auth.contoso.com
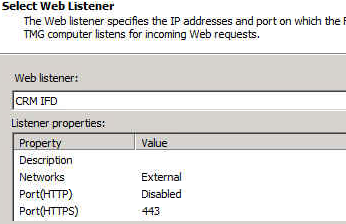
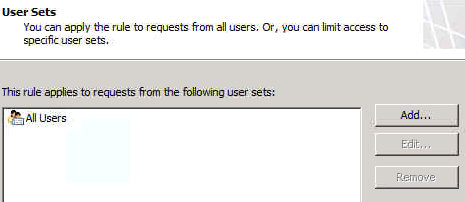
Select the web listener
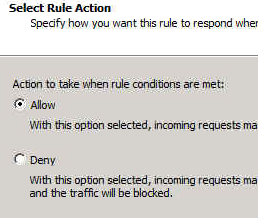
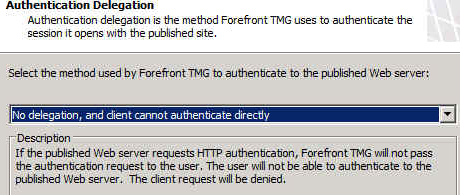
Leave at defaults and click next


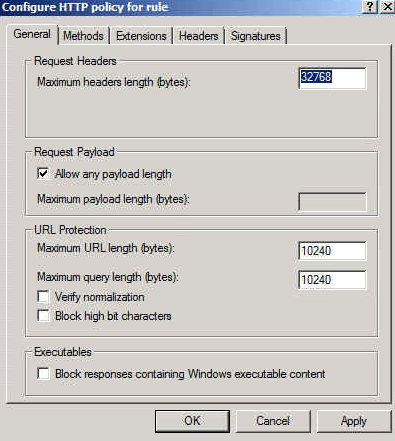
So when the rule is created, You need to right click on the rule and select “configure http”

And then untick  “Verify normalization” & ” Block high bit characters”
Remaining Rules

There are 2 more rules for CRM. So we simply copy and paste the rule we just created and edit the ‘to’ tab and ‘public name’ tab and add in dev.contoso.com and orgname.contoso.com

We copy and paste the rule again for adfs except as well as editing the to & public name tab we will also edit the computer ip and change it to 192.168.0.2 so that traffic for this rule is directed to the adfs server.
ADFS Login Page
Here is a great blog post on how to customise the ADFS login page to include a corporate logo. 


My thanks to Paul Mc Guinness who helped me get this working 🙂 

Office 365 Support for Windows Server 2012


I recently installed an ADFS Server farm on Windows Server 2012 but when I tried to federate to Office365 via the Microsoft Onlien Services Powershell Module it would not work!


The reason for the error is that in ADFS 2012 the cmdlets are surfaced by a module instead of a snapin, and the MSOnline cmdlets are hardcoded to load the old snapin which was available in ADFS 2.0. You can work around this issue by creating your own reference in the registry to the ADFS module as a snapin.
To do so, copy and paste the items below into notepad and save them as a .reg file and then execute.


Windows Registry Editor Version 5.00

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\PowerShell\1\PowerShellSnapIns\Microsoft.Adfs.PowerShell]
“ApplicationBase”=”C:\\Windows\\ADFS”
“Version”=”6.2.9200.0”
“AssemblyName”=”Microsoft.IdentityServer.PowerShell, Version=6.2.0.0, Culture=neutral, PublicKeyToken=31bf3856ad364e35”
“Description”=”This powershell snap-in contains cmdlets used to manage Microsoft Identity Server resources.”
“PowerShellVersion”=”1.0”
“ModuleName”=”C:\\Windows\\ADFS\\Microsoft.IdentityServer.PowerShell.dll”
“Vendor”=”Microsoft”

You can now use Windows Server 2012 for Single Sign on to Office365 🙂

Please note :  This solution is not supported by Microsoft. It is my understanding that a new Microsoft online services powershell module will be available for download when the new Office365 is generally available in Q1 of next year.

Enabling serialized hyper-v virtual machine backups in dpm

Here is an excellent blog posting by Matthew Hodgkins describing with screen shots on how to enable serialized hyper-v virtual machine backups in dpm.

So I would say follow Matthew’s Blog article , However I would make one slight change.

Copy the text below and save is as a .bat file and schedule the task to run the .bat file.

powershell “& {set-executionpolicy -executionPolicy bypass -force}” 

powershell “& “C:\Datascripts\ListVMsOnClusterForDPM.ps1”


Enabling serialized backups will prevent the following DPM error occurring.

Failed to prepare a Cluster Shared Volume (CSV) for backup as another backup using the same CSV is in progress. (ID 32612 Details: Back up is in progress. Please wait for backup completion before trying this operation again (0x8007173D))