Quest Migration Migration Manager Unable to migrate SID history

One of my colleagues Mark Doyle highlighted an issue with QMMA for Windows Server 2019 and 2022 domain controllers. Without these commands run on the 2019 and 2022 domain controllers the DSA agent server could not successfully migrate user accounts and SID history.

So my colleague Mark Doyle stuck at it , and even the Windows Server 2019 or 2022 firewall may state that it is off, it kind of isn’t.

So to resolve this issue we had run a couple of commands on the new 2919\2022 domain controllers and the problem was solved , so here are the commands.

1.netsh advfirewall firewall add rule name=”Quest Migration Manager Agent” dir=in action=allow program=”%SystemRoot%\System32\AelAgentMS.exe”

2.netsh advfirewall firewall add rule name=”Quest Migration Manager Agent” dir=in action=allow program=”%SystemRoot%\System32\AelAgentMS64.exe”

Now we can migrate SID history with user accounts,

How to migrate Teams Sites from Office365 tenant to another Office365 Tenant using Migration Wiz

This image has an empty alt attribute; its file name is image.png

I have been working very closely with BitTitan for a number of years and BitTitan have been working very closely with Microsoft with the development of their Teams migration service.

The service was updated towards the end of August and this update brought a large number of enhancements which can be reviewed HERE

For years I have been migrating Office365 Tenants to other Office365 tenants and the problem still remains whereby a custom domain like contoso.com cannot exist in two Office365 tenants at once. So during acquisition or merger migration projects at what point do you migrate the Microsoft Teams sites. My recommendation is to take care of the following data sources first with the Migration Wiz user migration bundle.

Primary Mailbox
Archive Mailbox
OneDrive for Business
Outlook switch over via deployment pro.

Once the data sources above have been migrated , I would recommend that Outlook Web App access to the legacy source tenant mailboxes is blocked via running the following command

Get-Mailbox -resultsize unlimited | Set-CASMailbox -OWAEnabled $false
Get-Mailbox -resultsize unlimited | Set-CasMailbox -ActiveSyncEnabled $False

The official MigrationWiz migration guide is available HERE
Also follow this ARTICLE and setup the  Teams-FullControlApp in each source tenant.
I recommend that you use the autodiscover method to populate the project as this will also identify any incompatible items in Teams sites or channels

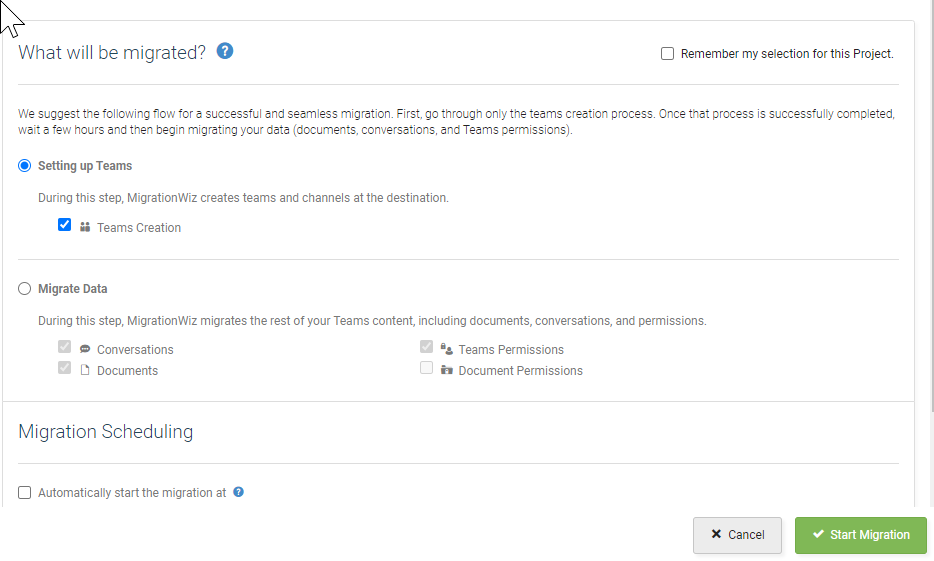
First step is to create the teams site in the target tenant , and do this 24 hours in advance

What_will_be_migrated_Teams.png

Next Step is to do the data migration

Validate the data and then remove the Teams licenses from the users in the source tenants with the following powershell commands. Create a new variable for each Offfice365 licensing sku that contains Teams.

Get-MsolAccountSku

$acctSKU=”contoso:O365_BUSINESS_PREMIUM”
$x = New-MsolLicenseOptions -AccountSkuId $acctSKU -DisabledPlans “TEAMS1”

$acctSKU2=”contoso:TEAMS_EXPLORATORY”
$x = New-MsolLicenseOptions -AccountSkuId $acctSKU -DisabledPlans “TEAMS1”

$acctSKU3=”contoso:O365_BUSINESS_ESSETIALS”
$x = New-MsolLicenseOptions -AccountSkuId $acctSKU -DisabledPlans “TEAMS1”

$acctSKU4=”contoso:O365_BUSINESS_ESSENTIALS”
$x = New-MsolLicenseOptions -AccountSkuId $acctSKU -DisabledPlans “TEAMS1”

Get-MsolUser | Where-Object {$_.licenses[0].AccountSku.SkuPartNumber -eq ($acctSKU).Substring($acctSKU.IndexOf(“:”)+1, $acctSKU.Length-$acctSKU.IndexOf(“:”)-1) -and $_.IsLicensed -eq $True} | Set-MsolUserLicense -LicenseOptions $x

And now all the Teams sites have been migrated and there is no chance of split brain because the Teams license has been removed from the source tenanat.

One really important point to note: MigrationWiz match users from the source to the destination based on the user prefix which is so useful when you are moving one domain from an Office365 tenant to another for example in a merger or aquistion.


Quest Migration Manager for AD – UPN change mid project

I recently encountered a unique scenario when using Quest Migration Manager for Active Directory. I was in the process of migrating 3 AD Forests into a new AD Forest. I had already migrated 1200 users into the new AD Forest and at the time of migration the UPN’s were contoso.com.

My customer then decided to change all UPN’s and primary smtp domains to @fabrikam.com in the middle of the project. This caused a big problem when computer accounts were being migrated. After the computer account had completed migration to the new domain, the user’s UPN was @contoso.com. Which meant the user had to change their UPN to login instead of just simply entering their existing AD password that they were previously using.

So how do we resolve this issue.Right click on the properties of the domain pair as per image below
Next change target domain to contoso.com or a fqdn of a domain controller in contoso.com

Next modify the security settings and set the domain suffix to fabrikam.com
Finally stop and start the synchronization task.

Once this has been completed, when computer accounts are migrated the correct UPN will be populated and users simply need to enter their existing AD password.

Transitioning to Outlook Mobile

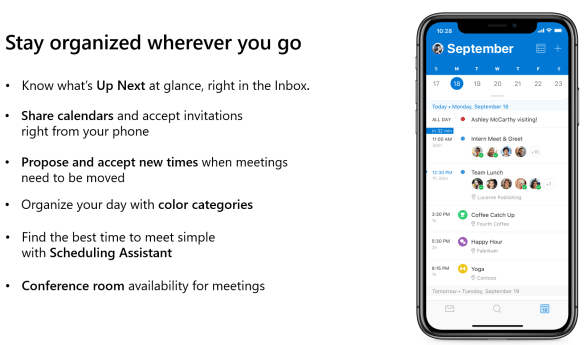
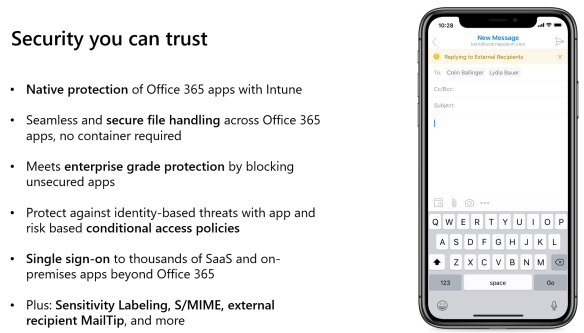
I always recommend the Outlook mobile client to my customers as this application can be included in an Intune app configuration & protection policy to protect and encrypt corporate data.

One of the features that the native IOS & Android mail client provides to end users is the illusion that the global address list of the organisation that they work for is in their native contacts. So when an end user searches for users in their company they expect to get the contact information instantly. Users must use Outlook Mobile.

End users mostly complain about loosing this feature but the argument is security comes first and Outlook Mobile is more secure!  It is very difficult to find the balance between security and productivity.

Android Outlook Mobile Cheat Sheet
IOS Outlook Mobile Cheat Sheet
Deploying Outlook for iOS and Android app configuration settings

Why use Outlook Mobile?

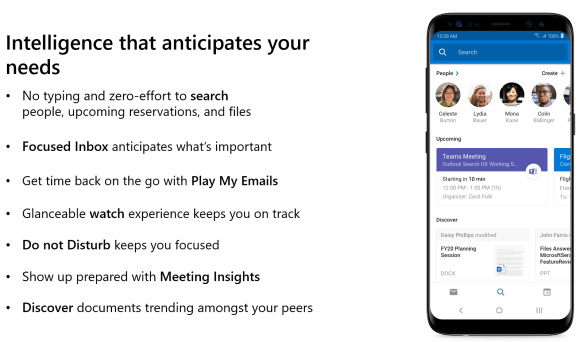
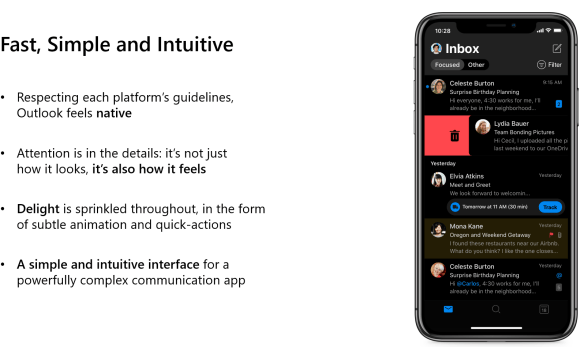
Content via Ignite 2019 Slide Deck

  • Consistent new features and security patches from Microsoft
  • In BYOB scenario , Corporate email profiles are encrypted via Intune App Protection policy
  • Azure Information Protection integration
  • Sensitivity Labels
  • Add a share mailbox to Outlook Mobile


Maintaining Exchange on-premise storage during migrations

Now that Microsoft have announced that Exchange 2010 support will end in October 2020 a lot of organisations are moving to Exchange 2016, 2019 or hopefully Exchange Online.

For enterprise organisations , the migration topology will include two Exchange 2016 servers that are load balanced via an F5 , Citrix Net Scaler or my preferred choice a Kemp load balancer. Autodiscover services for the smtp domains will be transferred to the new virtual IP and the service will be provided by the new Exchange 2016 servers that will proxy access requests to Exchange 2010 hosted mail resources.

The new virtual IP for load balancing services will become the target for the Exchange Online migration endpoint.

The Exchange Online Hybrid wizard licenses the new Exchange 2016 servers as part of the Hybrid configuration process , the Hybrid license does not permit the hosting of mailboxes. One of the problems with Exchange server since Exchange 2013 is log file growth. This post will demonstrate a scheduled task i always create on Hybrid servers.

The task schedules Edward van Biljon script available to download HERE

These log files are mostly IIS log files and not Exchange database log files as no mailboxes are hosted on the Hybrid server. But if an organisation is moving thousands of mailboxes to Exchange Online and not clearing down these logs, then they will run into issues. I have often reclaimed 20 -30GB of disk storage from running this script as a scheduled task.

Drawing1

The next section to consider is Exchange Database logs. Most vendors like

  • Commvault
  • Veeam
  • Veritas

perform an excellent backup service and are typically scheduled to run outside of business hours. Exchange backups are critical to truncate logs and become even more critical in an Exchange DAG. I have worked on previous projects that migrated Lotus Notes or Groupwise to Exchange and the log files grew too quick and could not wait till the daily evening backup. This issue can also arise in Exchange Hybrid native migrations due to the volume of traffic being migrated.

Most Exchange backup vendors communicate with VSS , It is critical that Exchange truncates the mailbox database logs , as there will be corruption in the databases’ if Exchange cannot perform this task.

If there is a scenario where the Exchange database and log volume is running out of space , Microsoft have an excellent utility called diskshadow which has been around for a long time. So essentially we trick Exchange into thinking a full backup has been performed and here are the simple steps if an Exchange Server database was installed on the system volume.

DiskShadow

This process should only be used in emergencies, Business as Usual backup schedules should normally ensure Exchange volumes do not run out of space but during migrations from an Exchange 2010 to Exchange Online or Lotus Notes to Exchange on-premise or online , the log files fill up really quick and even more so if there 3 or more databases that are members of a DAG

The final option for reclaiming space is offline de-fragmentation databases to claim white space. And only choose this option when all mailboxes have been migrated as it can take a long time and requires downtime.