Replacing TMG with IIS ARR for an Exchange Hybrid

On September 12th 2012 Microsoft announced that the TMG Forefront 2010 product will be discontinued. Microsoft obviously had to replace this product with alternatives. 
One of those products is the Web Application Proxy feature in Microsoft Windows Server 2012 R2   Web Application Proxy Deployment Guide 
Another product which was was released was Microsoft Application Request Routing 3.0 
This product plugs into IIS and can act as a reverse proxy to publish Exchange 2013/2010.
The Exchange Team Blog have a three part article on how to set it up and install it
Part 1 , Part 2 , Part 3 

There is an excellent Article on the Office365 community site on how to configure TMG 2010 for an Exchange Hybrid scenario.

And the key paths that require publication from the Hybrid Server are 
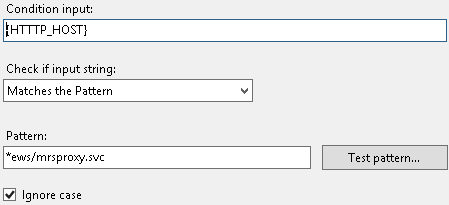
  • /ews/mrsproxy.svc
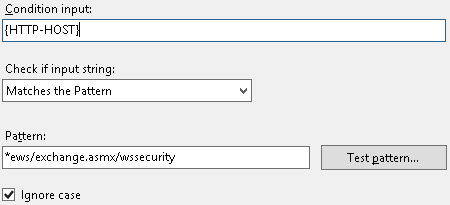
  • /ews/exchange.asmx/wssecurity
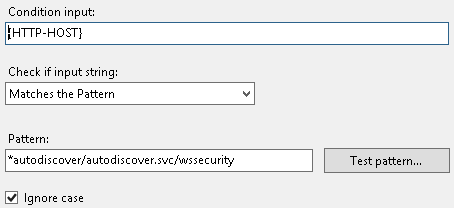
  • /autodiscover/autodiscover.svc/wssecurity
  • /autodiscover/autodiscover.svc
So how do we get these paths working in IIS ARR?????

The following 4 images are how we add the paths into the https url re-write section of IIS ARR
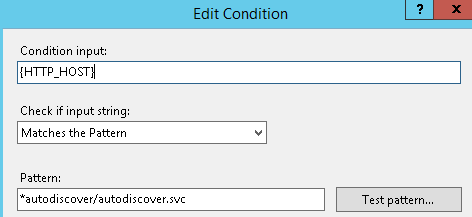


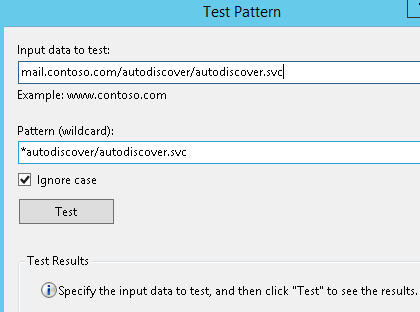

And then finally to test the path you enter the public url as per the image above mail.contoso.com/autodiscover/autodiscover.svc and when we press test.
GREEN LIGHTS APPEAR 🙂 

The main purpose of this blog was to help people understand how to get different path types into IIS ARR as it took me a bit of time to configure. A server 2012 R2 server can be provisioned in minutes in the right environment. Publishing Exchange Hybrid services like this from a DMZ is in line with Microsoft Best Practices.

Converting Office365 Cloud Identities into Managed Identities

There are three core identity scenarios in Office365 as illustrated above. I created a previous blog post on how to covert cloud identities to federated identities which can be viewed HERE

To convert cloud identities to managed identities with password sync can be quite simple by changing the users UPN and also matching the user’s UPN with their primary smtp address.

However , How many time have you received the dreaded email from Microsoft like below

Sean
Ofarrell
Unable to update this object because the following attributes associated with this object have values that may already be associated with another object in your local directory services: [ProxyAddresses SMTP:sean.ofarrell@contoso.com]. Correct or remove the duplicate values in your local directory. Please refer to http://support.microsoft.com/kb/2647098 for more information on identifying objects with duplicate attribute values.

So you search active directory and exchange online for conflicts but cant find any which will probably drive you CRAZY. So here is how to fix it.

I will demonstrate how to fix it for one user
It is very important that WAAD is not running when running these powershell commands.

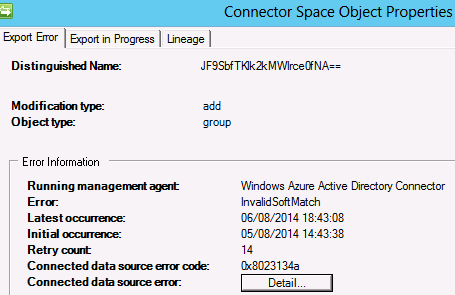
The image below is a synchronization error message from sean.ofarrell@contoso.com in WAAD

So to fix this we copy the distinguished name and run the following command.

set-MsolUser -UserPrincipalName sean.ofarrell@contoso.com -ImmutableID JF9SbfTKlk2kMWlrce0fNA==

Using Azure RMS with Office365

How to perform WAAD Manual Sync

WAAD version 4.3.647.0 seems to have moved the powershell module for manual syncs. To put the shortcut back on the desktop of your WAAD Server. Simply create a new shortcut and paste in the details below and then type start-onlinecoexistencesync to perform a manual sync

powershell.exe -noexit -noprofile -file “C:\Program Files\Windows Azure Active Directory Sync\DirSync\ImportModules.ps1”

How to enable Yammer SSO without ADFS

It would be great if when you click the Yammer icon in the Office365 services ribbon it actually signs you into Yammer rather than redirecting you to Yammer.com.

This blog will detail how to setup single sign on to Yammer via Microsoft Windows Azure Active Directory. When SSO for Yammer is enabled with Azure AD there is no on premise ADFS requirements.

Every Office365 Subscription also has a Windows Azure tenant in the background.When signed into an Office365 tenant , open a new tab and browse to this URL https://manage.windowsazure.com/ and signup for a free trial. 

You will need a credit card  when signing up however there will be no charge to the credit card.

  • Browse to the Active Directory section in the Azure Management Portal and then select
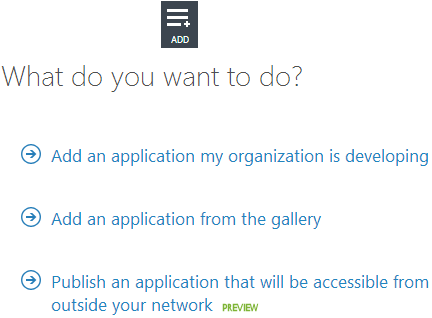
    “Add Application”  and “Add an application my organization is developing”
    as per the image below.
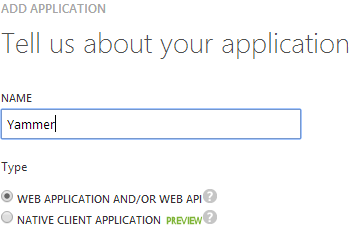
  • Name your application as per image below
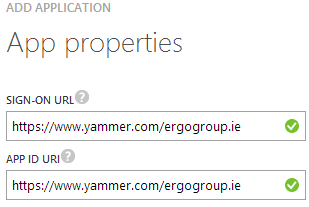
  • Then enter your sign-on url & app id uri as per image below
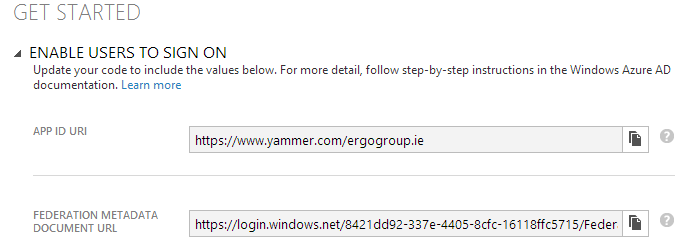
  • You then select “ENABLE USERS TO SIGN ON” and then browse to the “FEDERATION METADATA DOCUMENT URL” and save the metadata xml file as per image below.
  • Next we need to connect Windows Azure Active Directory via powershell and run the following commands
Import-Module MSOnlineExtended -Force
$replyUrl = New-MsolServicePrincipalAddresses –Address “https://saml.yammer.com/sp/ACS.saml2”
New-MsolServicePrincipal –ServicePrincipalNames @(“yammer/sso”) -DisplayName “Yammer Federation” -Addresses $replyUrl

  • The command will output an “AppPrincipalId” take note of this value and save it into a text file.
  • Then you will need to fill in the Yammer  SSO-Checklist.docx which you can download HERE
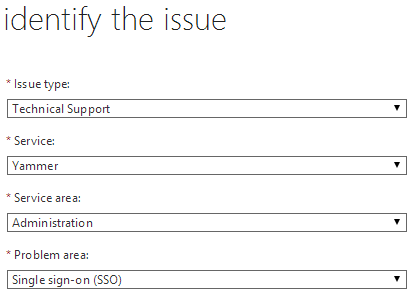
  • We now create a Service Request as per image below
  • We then create a compressed file that contains the FederationMetadata.xml, the AppprincipalId and the SSO Checklist and attach the file to the service request.
Once Yammer Support enable Single Sign On for your Yammer network. When you click on the Yammer link from the Office365 portal it will sign you into Yammer 🙂 Or when you browse to your Yammer SSO URL like https://www.yammer.com/contosogroup.ie
If you sign into Yammer , You can then open a new tab to access portal.microsoftonline.com or a Sharepoint Online site without having to re-authenticate. All this with no – on premise ADFS!

Credits: Billy Harris Microsoft