
How to lock down Office365 Global Admin access with managements scopes.

I have not posted a blog entry in quite some time, I have been crazy busy working for my new employer Evros and busy with my kids. I hope this blog will prove useful to anyone out there that follows my blog and promise a lot Blog posting to follow focusing on data protection, advanced threat analytics and AZURE

To help describe why an enterprise would like to lock down global admin access, I would like to describe a typical enterprise organisation and scenario.

Contoso.com is an enterprise organisation that consists of 15 companies. 
Contoso.com is the root AD Forest of the organisation and all other companies have their own child domains.
Contoso.com is the head office of the organisation and are responsible for data protection and governance within the organisation.
AD Connect synchronizes the root forests and child domains.

Contoso would like to remove global admin privileges from ICT Admin staff in one of the organisation’s companies Fabrikam and grant the ICT admin staff some custom Exchange Online administration privileges. The Fabrikam ICT admin staff must also have the ability to log Office365 service requests.

The following steps are required to lock down the Fabrikam ICT staff access to Office365 as per Fabrikam’s parent company Contoso’s new security and data protection policies.

#####################Exchange Management Shell############################
####Create Management Scope
New-ManagementScope -Name “EO-FABRIKAM” -RecipientRestrictionFilter {customattribute10 -like “FABRIKAM“}
####All mail enabled objects  in the Fabrikam child domain will have the value ‘Fabrikam’ added to Active Directory attribute: Extenstionattribute10
####Create a Role Group
New-RoleGroup -Name “EO-FABRIKAM” -Roles “User Options”, “Address Lists”, “Distribution Groups”, “Team Mailboxes”, “Mail Recipients”, “Reset Password”, “Mail Recipient Creation”, “Message Tracking”, “Move Mailboxes”,”Migration”,”Retention Management”,”UM Mailboxes”, “UM Prompts” , “Unified Messaging”    -Members “EO Fabrikam Admins” -CustomRecipientWriteScope “EO-FABRIKAM” -ManagedBy “Organization Management”

####Note: When assigning the members to a security group. The security group must be a mail enabled security group.

####################Windows Azure Active Directory###########################
 

Function

Commandlet

Import CSV

$Users = Import-Csv “CSV PATH“

Assign Role

$Users | ForEach-Object {Add-MsolRoleMember -RoleMemberEmailAddress $_.UserPrincipalName -RoleName “Service Support Administrator”}

####Note: It is not possible to assign service administrator roles per security group

############################Summary####################################

Fabrikam ICT admins can access the Exchange Online Control Panel via this URL: https://outlook.office365.com/ecp
Fabrikam ICT admins can log Office365 service request via this URL:

#############################Next Steps##################################
The next steps would be to create similar management scopes and role groups for SharePoint Online and Skype for Business. (New Blog Post to Follow)
Once Contoso have locked down access for all the companies within their organisation the next step will be developing compliance and governance policies in the Security and Compliance center in Office365


Synchronize an Exchange Online Mailbox with a different Active Directory Forest.

I recently worked on a project whereby I was migrating a Global Company that owned a number of business and they wanted to break down the barriers between the different brands and all collaborate under a new brand in Office365.

I synchronized a number of forests from around the world into the organization’s Office365 tenant using the new Azure Active Directory synchronization tool. 

One of the businesses shared their Exchange Server (Business A)  with another business (Business B) and to migrate their mailboxes I implemented an Exchange Hybrid and migrated the mailboxes into Exchange Online. 

Business A Active Directory was authoritative for Business B mailboxes. So how do we disjoin them from Business A and synchronize them with Business B , so that Business B can perform identity management on their own Active Directory Forest.

So the following steps explain how to do this. This can of course be scripted if there were hundreds or thousands of users.

  1. Run this command on Business B Active Directory Forest to obtain all user’s immutable ID
    ldifde -f con -r userprincipalname=sean@contoso.com -l objectguid
  2. Then on in the AAD tool stop synchronizing the users’ from Business B
  3. This will then delete the users accounts, got to the Office365 recycle bin and restore the user’s account. This will also convert the user’s account to a cloud identity.
  4. The run this command in  the ‘Windows Azure Active Directory Module for Windows PowerShell’ to convert the cloud user’s immutable id so that it matches the object guids obtained in step 1

    set-MsolUser -UserPrincipalName sean@contoso.com -ImmutableID I3/MGNcBbUWWVs+jXPTH4g==

  5. Finally their are some attributes that we need to match from Business A Active Directory Forest with each user’s account in Business B Active Directory

    msExchAddressBookFlags
    msExchMailboxGuid
    msExchMasterAccountSid
    msExchRemoteRecipientType

  6. No we are ready to sync the OU with the AAD tool from Business B and Business B Active Directory will be the authoritative Active Forest for these mailboxes. 

Script to add legacyexchangedn as x500 alias into AD user object for Exchange Online

If a scenario existed whereby there was a non exchange hybrid like lotus notes or group wise messaging platform and some users were using Office365 and co-existence was achieved by uploading all of the onpremise users’ as external contacts. Office365 users recipients have messages forwarded to from the source messaging platform. 

As you begin to convert the onpremise users’ to federated or managed users. You need to capture that user’s legacyexchangedn and ingest it into the users’ AD users’ proxyaddresses attribute as an x500 alias to prevent potential NDRs from existing Office365 users.

So run this Exchange Online command

get-mailcontact – resultsize unlimited | select-object legacyexchangedn,primarysmtpaddress | export-csv “csv file path” delete the first line 1 from the output of the csv

Then download this SCRIPT and edit the following lines

  • edit line 11 and enter your domain name
  • edit line 25 and enter your domain name
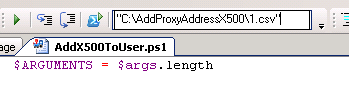
Then hold down shift and right click on the csv and select copy as path and paste the path into the window as per the image below and press the green play button.

This script will then search the root of the domain based on the domain name and mailnickname and add an x500 alias into the users’ proxyaddresses attribute which will then be synced to Office365 via dirsync

So before the OU containing the AD user objects that needs to be synced you will need to run this command as there will be conflicts in dirsync.

import-csv “C:\Users\admin\Desktop\contacts to be deleted\contacts.csv” | Foreach-Object{Get-Mailcontact $_.primarysmtpaddress | remove-mailcontact -Confirm:$false}

Credit : Eduardo Martin

Quest Powershell Script to change UPN for Office365

I normally use AD Modify to modify users’ UPNs. But it is only really practical when you are changing the UPN’s per OU. 

Lets say you were migrating from a different messaging platform , like Lotus Notes or GroupWise. But AD had the mailnickname attribute populated and the correct UPN added into your AD. To run the script you need to do the following

  • Create a csv mail.csv and place it in the root C:\mail.csv. The heading of the csv will be ‘mail’ and then all the mailnicknames like sean@contoso.com
  • On line 29 add in the distinguished name of the domain/forest scope
  • Create a folder C:\logs to analyse any errors
  • Watch out for ‘ which are acceptable characters in a smtp email address but unacceptable as a UPN in Office365.
  • The script can be downloaded HERE.
The author of the script is a colleague of mine Adam Smith

Bulk Uploading Mailboxes to Exchange Online and assigning licenses


Microsoft have made it really easy to perform bulk migrate migrations and assign licenses in Exchange Online.

You can export a csv and use it twice. The first csv will have the following headings

emailaddress
sean.ofarrell@contoso.com
ciaran.ofarrell@contoso.com
dean.jones@contoso.com
tecnicalfellow@contoso.com 

You can then upload the file then via the following option in Exchange Online 


And then to assign the licenses use the same csv but change the top heading to userprincipalname like below

userprincipalname
sean.ofarrell@contoso.com
ciaran.ofarrell@contoso.com
dean.jones@contoso.com
tecnicalfellow@contoso.com 

Connect to Office365 via the Windows Azure Active Directory Module for Windows PowerShell and do the following.


# First of all paste in the following variables

$AccountSkuId = “contoso:EXCHANGESTANDARD”
$UsageLocation = “IE”

# The paste the command in below with the correct CSV file path

$Users = Import-Csv “C:\Users\contoso\Desktop\Scripts\Import_users.csv”
$Users | ForEach-Object {
Set-MsolUser -UserPrincipalName $_.UserPrincipalName -UsageLocation $UsageLocation
Set-MsolUserLicense -UserPrincipalName $_.UserPrincipalName -AddLicenses $AccountSkuId
}

And if you wanted to assign Exchange Online P2 Licenses then run the following commands,

# First of all paste in the following variables

$AccountSkuId = “contoso:EXCHANGEENTERPRISE”
$UsageLocation = “IE”

# The paste the command in below with the correct CSV file path

$Users = Import-Csv “C:\Users\contoso\Desktop\Scripts\Import_users.csv”
$Users | ForEach-Object {
Set-MsolUser -UserPrincipalName $_.UserPrincipalName -UsageLocation $UsageLocation
Set-MsolUserLicense -UserPrincipalName $_.UserPrincipalName -AddLicenses $AccountSkuId
}

If you are using waad and want to assign a user with a P2 license an archive then you need to populate the AD attribute for the user “msExchRemoteRecipientType’ and change the value to 3. This can be done in bulk via ADMODIFY or Powershell