There have recently been an increased amount of brute force password spray attacks against M365 \ Azure AD tenants.
The obvious protection is to implement (MFA) Multi Factor Authentication as the first line of defence.
A complex 8 character password that is not protected with MFA can be cracked in 24 hours or less.
I recently worked on a project where some M365 user accounts were brute force password sprayed attacked over 20,0000 times in a single month.
A lot of organisations make the mistake of having a ‘Meet the Team’ section on their corporate website, including the senior team member’s email addresses, which is one of the first places a bad actor will target.
Bruce force password spray attacks are not performed by human beings, they are performed by bots, hosted on private cloud networks or some public cloud networks……
A simple solution to protect an organisation against brute force password spray attacks is to enable Microsoft password less, gps authentication and biometric authentication via the Microsoft Authenticator application.
Conditional access policies that allow or block countries are not effective as a bad actor can simply mask their IP and pick any country code IP that they choose.
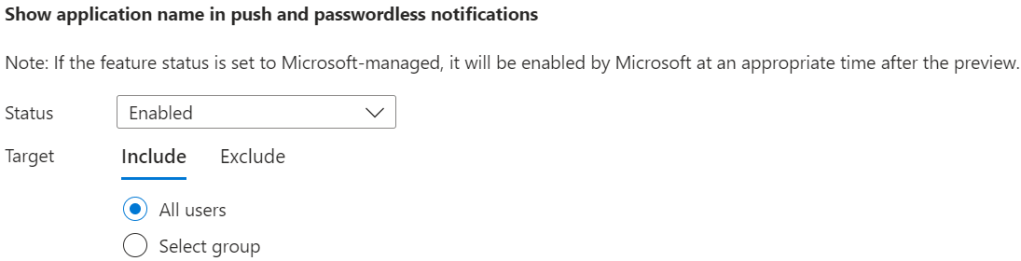
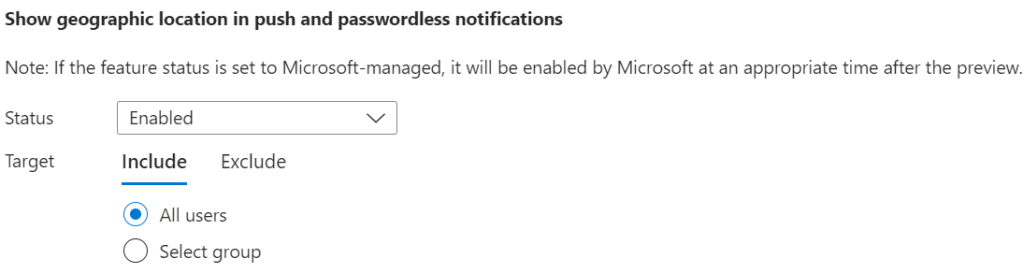
Microsoft Authenticator password less authentication mechanism To enable password less and GPS location authentication , please implement and test the following configuration. 1. Browse to Azure Active Directory\ Security \ Authentication Methods 2. Select Microsoft Authenticator
3. Enable and target a test group before enabling the feature for all users
4. Select the following 3 configurations
Microsoft Authenticator Application Configuration
The end user must enable phone sign in on the Microsoft Authenticator application. Currently, this can only be enabled for one password less account on Android, but multiple accounts on iOS.
End User Experience
No password
Click yes if you are in Dublin, no if the GPS notification is displaying an incorrect location. The GPS location, protection mechanism must be communicated to end users. Do not click yes if the GPS co-ordinates specifies Hong Kong, if you are in Dublin
The final step is to validate via biometric thumbprint on your Android or iOS device.
Summary
Brute force password spray attacks cannot succeed when the following authentication methods are in place.
1: Password less 2: GPS verification 3: Biometrics validation on the Microsoft Authenticator application
The end user experience is much more user friendly, and most importantly a lot more secure.
This blog post will focus on the triggers and actions available in the ‘Microsoft Defender ATP API’ and how Power Automate can, automate tasks using this API.
The number 1, recommendation is to use Microsoft Sentinel. In my view SIEM without SOAR is useless.
When can an organisation be truly ready to enable SOAR automation for Windows 10\11 endpoints?
The Microsoft portal security.microsoft.com/Vulnerability Management/recommendations section provides recommendations on all endpoint vulnerabilities.
How does this section of the Microsoft security portal, provide recommendations on devices that have not been enrolled into Microsoft Defender for Endpoint management? This can be controlled via the Microsoft security portal device discovery configurations.
Typically organisations do not transition, straight away to using (MEM) Microsoft Endpoint Manager to provide software update services.
A remediation task in MEM to update a version of Google Chrome or Notepad ++, can only be actioned if, MEM is controlling software updates and if the latest versions of Google Chrome or Notepad ++ are available in the MEM Microsoft Windows application repository for Windows 10\11 devices.
I recommend that an organisation, responds to all security.microsoft.com/Vulnerability Management/recommendations, via their existing software update service prior to transferring update services to MEM. MEM provides excellent automated software update services to Microsoft software products, but can be quite cumbersome when it comes to updating 3rd party software products, like Google Chrome and Notepad ++
Some organisations, make the mistake, and think that enabling (MDFE) Microsoft Defender for Endpoint – auto remediation, will just work and protects endpoints from all threats.
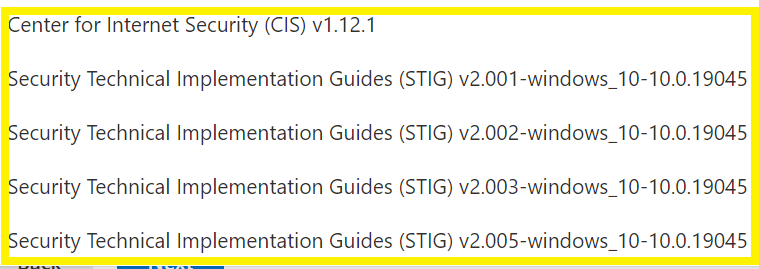
Run these baselines , my preference is the CIS security baseline and improve the security posture of an organisation’s Windows 10\11 devices as much as possible before implementing, Microsoft Defender for Endpoint – Auto Remediation, or Microsoft Defender automation tasks via Power Automate or Microsoft Sentinel.
The Microsoft : security.microsoft.com portal provides a service called ‘Custom detection rules’, however the frequency of ‘custom detection rules’ is ‘every hour’, which is not good enough.
Power Automate – automated protection via the ‘Microsoft Defender ATP API’
Firstly, there are two amazing blog posts that describe the process of using Power Automate on how to auto isolate, Windows 10\11 devices, based on their severity risk level.
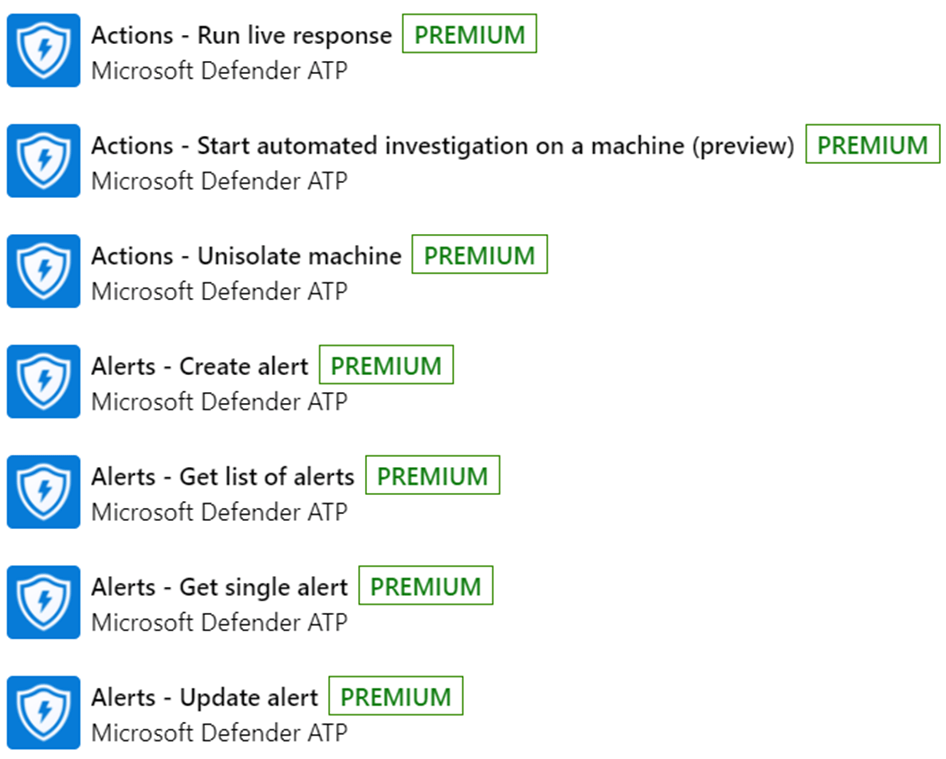
‘Microsoft Defender ATP API’ Actions The following actions, clearly illustrate the power of the ‘Microsoft Defender ATP API’, when an organisation has improved their security posture with Windows 10\11 devices. With some Power Automate or Microsoft Sentinel runbooks, these actions can enable an organisation to protect a bespoke line of business work flow on endpoint devices.
Some organisations may say, ‘Why MDFE, cannot, just provide this protection as standard’, and the simple answer is, every organisation’s line of business applications or workflows are different and require, custom, granular control, that the ‘Microsoft Defender ATP API’ can provide via Power Automate but, most preferably : Microsoft Sentinel.
The following images outline the actions that are possible using the ‘Microsoft Defender ATP API’
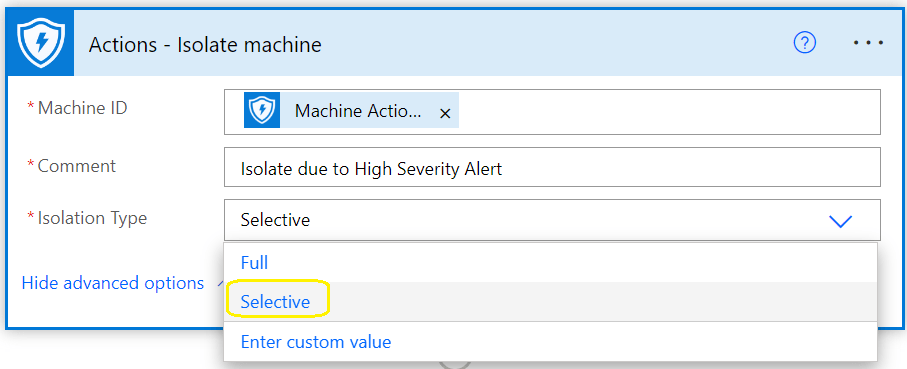
Microsoft Defender Auto Isolation new Feature It is now possible to ‘isolate’ devices but continue to allow end users to use ‘Microsoft Outlook and Teams’
This feature, ensures that end users can continue to remain productive in their daily work routines when using Windows 10\11 devices, yet be isolated from their corporate network, probably the best use case, is to prevent the spread of ransomware or Mimikatz credential theft.
How is this Auto Isolation feature to allow users to continue using ‘Microsoft Outlook and Teams’ controlled in the ‘Microsoft Defender ATP API’
I always find using Microsoft Azure Active Directory dynamic groups much easier to use when assigning policies, for example Defender for Endpoint onboarding policies via Intune.
Microsoft Defender for Endpoint included with M365 licensed user rule syntax
I have created Blog Posts about this in the past, but Microsoft continue to innovate and develop new technologies that can simplify an organisation’s data classification journey.
GDPR The European Union introduced a new regulation called GDPR in 2016. There is a new
Wikipedia: https://en.wikipedia.org/wiki/General_Data_Protection_Regulation Regulation on the protection of natural persons with regard to the processing of personal data and on the free movement of such data, and repealing Directive 95/46/EC (Data Protection Directive).
The European Union’s GDPR regulation was a big step in forcing organisations to consider implementing and controlling personally identifiable information.
In Ireland some of the core unequally identifiable attributes could be as follows. -PPS – Personal Public Service Number -Driving License -Passport -Mobile Phone Number -Date of Birth
The unequally identifiable attributes mentioned above are directly related to individuals.
When it comes to an organisation’s intellectual property, how is this their data protected. It could be for example.
-Milk – The ingredients and process of manufacturing and distributing milk -Bread – The ingredients and process of manufacturing and distributing bread -Beer – The ingredients and process of manufacturing and distributing beer
Data Classification and protection is such a critical requirement for any organisation, and most organisations find it difficult, on where to begin their data classification journey. Not knowing where to begin a data classification journey can often pause or completely halt an organisation’s data classification journey. Microsoft have developed multiple solutions to try and speed up and enhance an organisation’s data classification journey.
A lot of organisations are not aware of the amount of compliance technologies, machine learning, and artificial intelligence that Microsoft Purview can provide, and organisations are typically licensed for these services and not using them.
The way forward: DORA sets a benchmark
DORA is expected to be published in the Official Journal of the European Union by the end of 2022 after final adoption by the European Parliament and other procedural steps are completed. Following the publication, there will be a 24-month implementation period before the rules enter into force, therefore, the rules under DORA will apply as of late 2024 at the earliest—thus allowing Microsoft and financial institutions to ensure compliance with the new rules ahead of that time. During the implementation period, the Regulatory Technical Standards (RTSs) will also be under development to facilitate DORA’s implementation. The RTSs are expected to be completed ahead of DORA application.
The key requirements under DORA cover the following: ICT risk management, ICT-related incident reporting, digital operational resilience testing, and oversight of critical ICT providers. The legislative framework will also require compliance by critical ICT third-party service providers.
At Microsoft, we support our financial services customers and will continue doing so under DORA implementation—specifically, but not limited to the following key areas:
ICT risk management: DORA establishes a comprehensive management mechanism of ICT risks with which financial entities would be required to comply—including the identification, protection and prevention, detection, response, and recovery of such risks in scope. Microsoft already provides a broad set of built-in ICT risk management capabilities in our services today. This includes, by way of example: Microsoft Defender for Cloud, Microsoft 365 Service Health Dashboard, and Microsoft Secure Score.
ICT-related incident reporting:DORA will harmonize the classification of incidents while streamlining the reporting processes to develop a more systematic approach to monitor, control, and follow-up on such incidents. DORA foresees a coordinated approach to ICT incident reporting and tackling reporting overlaps such as the NIS2 Directive. Microsoft provides such capabilities, such as with Microsoft Defender.
Digital operational resilience testing: DORA introduces digital operational tests that should be conducted on critical ICT systems and applications on an annual to triennial basis (regarding advanced threat-led penetration testing). This new testing approach will bolster the testing capabilities of financial entities—fostering timely recovery and business continuity. Microsoft already enables customers to do so through our penetration program. Learn more about the Microsoft Cloud Penetration Testing Rules of Engagement program.
Oversight of critical ICT providers: DORA foresees a communication mechanism between financial regulators and ICT critical service providers for the management of ICT third-party risks. Microsoft already partners closely with its customers and has ongoing and rich engagement with regulators—including audit and regulatory examinations. We think such processes should include inter-agency cooperation amongst other regulators not limited to Europe. For example, alignment and communication among the Bank of England and the United States Regulators (FDIC, OCC, Federal Reserve), would be helpful from a regulatory oversight perspective, drive synergies, avoid fragmentation, and maintain a level of clarity and communication that would benefit regulators and Microsoft alike.
Legacy on-premises data classification
Typical vendors like Broadcom (formally Symantec), Forcepoint (formally WebSense), McAffee, did a really good job of analysing on-premises data stores like ; file shares, sql databases, exchange servers. But these vendors were unable to bridge the gap between on-premises workloads and cloud workloads, most organisations work in a hybrid environment and host data between on-premises infrastructure and private or public cloud services.
Microsoft Windows Information Protection (WIP), previously known as enterprise data protection (EDP). Was a service that Microsoft introduced to provide data loss prevention services on Windows 10\11 devices. This service was quite difficult to configure and provide meaningful insights and recommendations to organisations. Microsoft then deprecated Windows Information Protection in July 2022.
What is the point or how effective is data protection without data classicisation?
Microsoft have bridged the gap between on-premises and cloud workloads with technologies that help organisations define their unique sensitive information using technologies like: -Advanced e-Discovery -Data Map and Data Catalog -Auto-classification -Microsoft Purview Insider Risk Management policies -Microsoft Purview Insider Risk Management -Microsoft Defender for Cloud Apps -Microsoft Purview document fingerprinting
Microsoft Classifiers A Microsoft Purview trainable classifier is a tool you can train to recognize various types of content by giving it samples to look at. Once trained, you can use it to identify item for application of Office sensitivity labels, Communications compliance policies, and retention label policies.
Creating a custom trainable classifier first involves giving it samples that are human picked and positively match the category. Then, after it has processed those, you test the classifiers ability to predict by giving it a mix of positive and negative samples. This article shows you how to create and train a custom classifier and how to improve the performance of custom trainable classifiers and pre-trained classifiers over their lifetime through retraining
Microsoft currently have 59 trainable classifiers such as – Wire Transfer – Profanity – Money Laundering
Custom classifiers can also be created for an organisation’s bespoke requirements.
Microsoft Endpoint Data Loss Prevention
Microsoft Windows Information Protection was a terrible service and it did not take long for Microsoft to retire the service.
Microsoft finally got it right, Microsoft Endpoint Data loss prevention is a superb service.
When implementing Attack Surface reduction policies. The following configurations should be set in audit mode to allow you to compile an inventory of Microsoft Word, Excel , Outlook etc, add – in child processes.
If you simply block all the of the options illustrated below, then can possibly block Microsoft Office add-ins.
A good way to analyse Microsoft Office add-ins, is to review endpoint analytics in the Microsoft Intune portal.
Start with audit mode, compile an inventory of what Microsoft add – ins, create child processes, analyse the audit mode for the three controls illustrated below via KQL queries and finally a risk assessment on all Microsoft Office add-ins, only then can you whitelist line of business Microsoft add-ins that have passed a risk assessment.