Series:This is Part 6 of 7 in my series on Microsoft Purview Insider Risk Management. New to the series? Start with the series guide, which summarises every part.
This is the question security leaders and data protection officers ask me most: is insider risk management something we have to do by law, or is it just a service Microsoft provides?
The short answer
No law names it. No Irish or EU law says you must use Microsoft Purview Insider Risk Management, or any particular product. It is a Microsoft service.
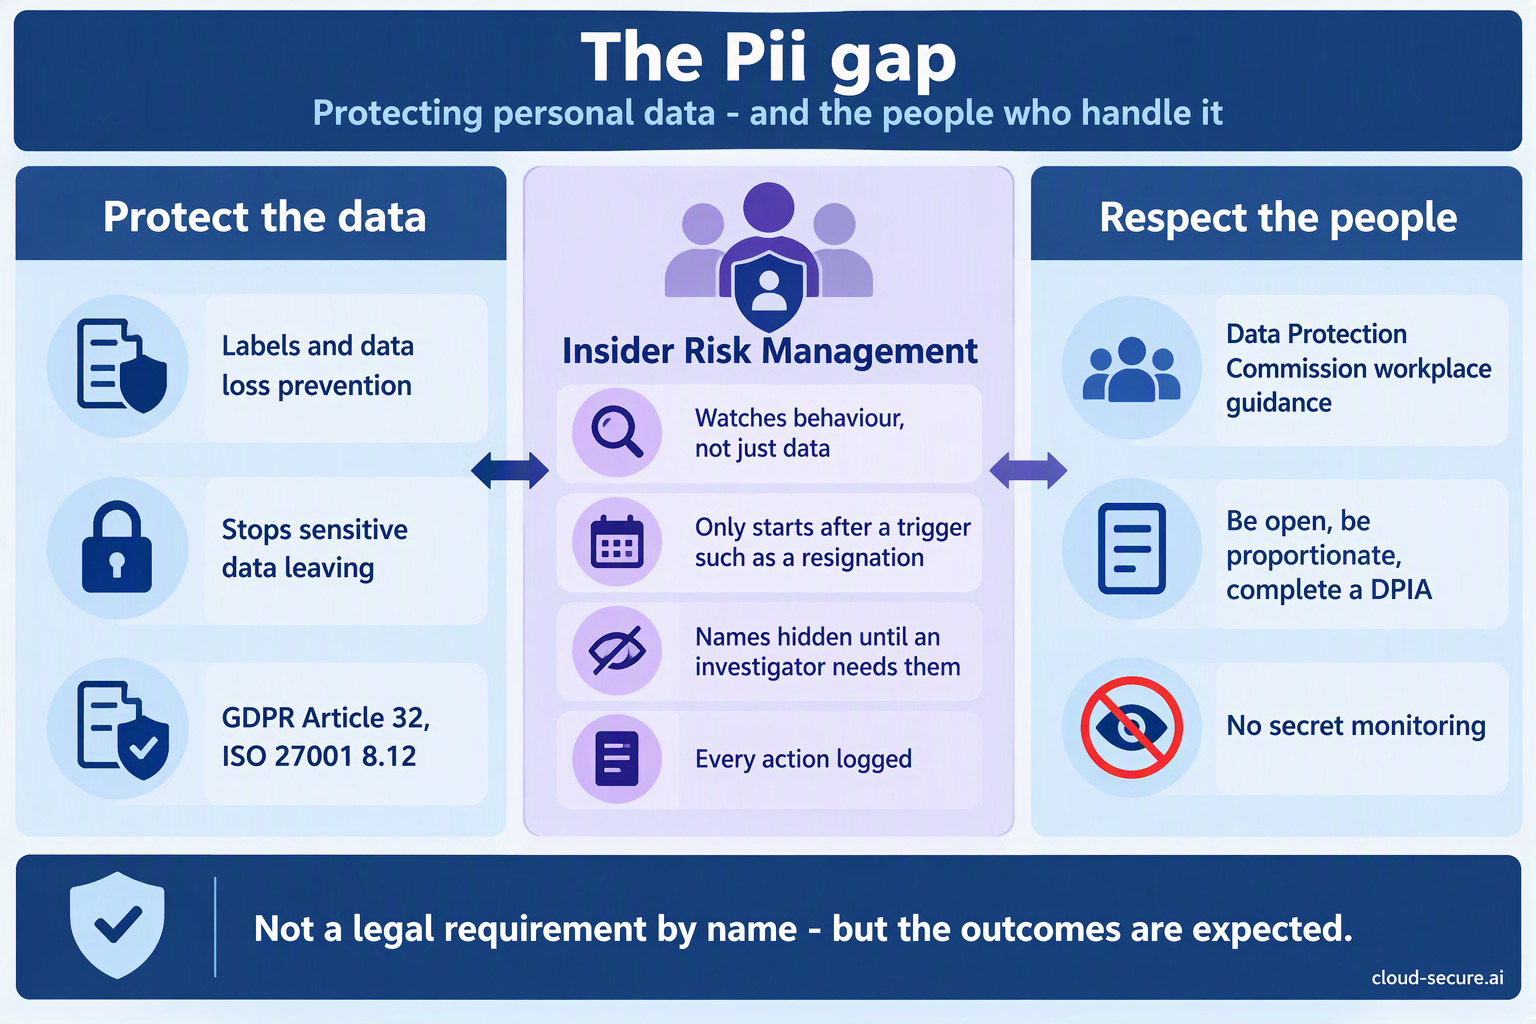
But the results it delivers are expected. The main rules and standards – GDPR, NIS2, DORA and ISO 27001 – all expect you to stop data leaking out, manage the security risk of people joining and leaving, and spot unusual activity. At the same time, data protection law sets strict rules on how you monitor employees. Insider Risk Management sits between those two pressures: protecting personal data, while respecting the privacy of the people who handle it.
Important: I am a security architect, not a lawyer. This section explains how the frameworks relate to Insider Risk Management. Get advice from your DPO and legal team on your own obligations.
What the laws and standards expect
Law or standard
What it expects
How Insider Risk Management helps
GDPR Article 32 (security of personal data)
Suitable technical and organisational measures to protect personal data, including from being shared without permission. Pseudonymisation is named as an example.
Spots insiders moving personal data out, and hides the identities of the people it monitors.
GDPR Articles 33 and 34 (breach reporting)
Tell the Data Protection Commission within 72 hours of becoming aware of a personal data breach, and tell the people affected if the risk to them is high.
Alerts and timelines tell you a breach has happened and show what left, when and how.
NIS2 Article 21(2)(i) (EU cybersecurity law)
Security around staff, control over who can access what, and managing company assets. Management boards are held accountable.
Links HR events such as resignations to data activity, and adjusts access automatically for risky people.
DORA (EU law for banks, insurers and other financial firms)
Managing IT risk, including quickly spotting unusual activity. Applies from January 2025.
Spots unusual behaviour and sends alerts to the security team.
ISO/IEC 27001:2022 (international security standard)
Controls 6.5 (security when people leave or change role), 8.12 (preventing data leaks) and 8.16 (monitoring for unusual activity).
Evidence for all three controls when auditors ask.
NIST SP 800-53 PM-12 (US government security standard)
An insider threat programme – one of the few standards that asks for one by name. Relevant if you supply the US government.
Provides the technology at the heart of an insider threat programme.
NIS2 in Ireland: NIS2 is an EU cybersecurity law that Ireland has not yet written into Irish law. A draft outline of the National Cyber Security Bill was published in August 2024, and in July 2026 the European Commission took Ireland to the EU Court of Justice over the delay. The National Cyber Security Centre is set to be the main regulator. The obligations are coming, and organisations it will apply to should be preparing now.
The PII gap
PII stands for personally identifiable information – anything that identifies a person, such as a name, address or PPS number. Most Purview projects focus on protecting that data directly: finding it, labelling it and stopping it leaving with DLP. That protects the data. It does not tell you when a trusted person, who is allowed to see that data, starts behaving in a way that puts it at risk. That is the gap Insider Risk Management fills.
But there is a second side to the gap. Monitoring employees means collecting information about them, which is itself covered by data protection law. The Data Protection Commission’s 2023 guidance for employers makes four points clear. Workplace monitoring must be open and proportionate – no more than is needed. Employers will find it hard to justify monitoring simply because it is in their business interest (known as “legitimate interests”). A data protection impact assessment (DPIA) – a written assessment of the privacy risks – is essential before monitoring starts. And secret monitoring should be avoided wherever possible. European court rulings point the same way: employees should be told in advance that monitoring may take place.
This is where Insider Risk Management is genuinely different from a surveillance tool. Its design lines up closely with those principles:
Data protection principle
How Insider Risk Management supports it
Transparency – be open about it
Policies watch activities you can describe to staff in your IT acceptable use policy and privacy notice. Built-in notice templates help you communicate with them.
Proportionality – no more than needed
People are only scored after an event such as a resignation. Policies can be limited to specific groups.
Pseudonymisation – hide identities
On by default. Names are only revealed to authorised investigators.
Limit who can see what
Separate role groups for the people who set it up, review alerts, investigate and audit.
Accountability – keep a record
Every action inside Insider Risk Management is logged, and a dedicated Auditors role group can review that log.
Purpose limitation – only use it for the stated reason
Each policy template has one clear purpose – data theft, data leaks, security breaches or risky AI use.
No secret monitoring by default
It uses activity that is already recorded, such as audit logs. It does not record keystrokes. Forensic evidence (screen recording) is optional and needs approval – treat it with particular care in your DPIA.
What you need to do
Complete a DPIA before switching on Insider Risk Management, and update it when you add new policies or features.
Write down your legal basis – the legal reason you are allowed to do this – and, if it is legitimate interests, show how you weighed your needs against employees’ privacy.
Update your IT acceptable use policy and employee privacy notice so staff know what activity may be monitored and why.
Involve HR, legal, the DPO and employee representatives early. The HR connector makes HR a stakeholder anyway.
Keep pseudonymisation on and keep the Investigators role group small.
Set retention for alerts and cases in line with your records policy.
Link it to the standards you follow – for example ISO 27001 controls 6.5, 8.12 and 8.16, NIS2 Article 21 and DORA – so the evidence is ready when auditors ask.
My view
No regulator will ask you whether you have switched on Insider Risk Management by name. But every standard above expects you to spot and deal with the risk it covers, and data protection law expects you to do it fairly and proportionately. Few tools do both as well.
And here is the uncomfortable question: after a departing employee walks out with a customer database, how do you explain to the Data Protection Commission that the control designed to catch it was already licensed, already paid for – and switched off?
What can DLP protect if nothing has been classified?
Very little. A DLP policy is only as good as the sensitive information types and labels behind it. If Contoso has never defined what its sensitive data looks like, DLP has nothing to look for.
Out of the box, Purview DLP recognises what Microsoft has already classified for every tenant: credit card numbers, PPSNs, IBANs, passport numbers, credentials. Useful, but none of it is Contoso’s. Not one built-in SIT knows what a Contoso project code, design specification, customer list or product roadmap looks like. Without classification, a DLP policy is left with two options:
Match on Microsoft’s built-in types only. Personal and financial data is protected; Contoso’s intellectual property walks straight past every rule.
Fall back on context alone. Block every attachment to an external domain, every upload to an AI app, every file copied to USB. That stops IP, and it stops the business with it. Users find a workaround within a week, and the policy is rolled back to audit within a month.
Blind or blunt: the policy either misses what matters or blocks everything. Classification is what gives it a third option – block what is sensitive and let everything else through.
The same applies to every control I have written about this month. I have blocked unsanctioned MCP servers, inspected traffic to AI apps, governed agents in Agent 365 and stopped credentials leaking from Exchange and Teams. Each of those posts answers the question where is this data allowed to go? None of them can answer the question that has to come first: what is this data? A network indicator blocks a destination whatever is sent to it. A Copilot policy can only exclude content that carries a label. Inline DLP can only block a prompt that matches a SIT.
The credentials post came closest to saying this. It works because Microsoft has already done the classification for you: the All Credential Types SIT ships ready-made, so the policy simply has to be switched on. Intellectual property gets no such head start.
This post covers the classification methods Microsoft Purview offers, the different types of DLP that act on them, where you can find sensitive data already sitting at rest, and how to put it all together around the asset that is hardest to protect and most damaging to lose: Contoso’s intellectual property.
Key terms
If you are new to Purview, these are the terms the rest of the post relies on:
DLP (data loss prevention) – policies that detect sensitive content and audit, warn or block when someone tries to move it.
SIT (sensitive information type) – a pattern Purview recognises, such as a credit card number: usually a regular expression (regex) plus supporting keywords.
Confidence level – how sure Purview is that a SIT match is real: Low (65), Medium (75) or High (85). More supporting evidence means higher confidence.
Proximity – how close, in characters, a supporting keyword must be to the pattern to count as evidence.
Sensitivity label – a tag such as Highly Confidential written into a file or email, which can also encrypt it.
EDM (exact data match) – matching on the actual values in your own data, such as real customer account numbers, rather than on a pattern.
Document fingerprint – a SIT built from a blank form or template, which matches any document written on it.
Trainable classifier – a machine learning model that recognises a type of document, such as source code or a patent.
Inline DLP – DLP applied to web traffic as it leaves, either inside Edge for Business or at the network through Global Secure Access (GSA), Microsoft’s cloud network security service.
MCP server – a service an AI agent connects to for extra tools or data.
Why the earlier controls worked
It is worth looking back at why the earlier posts produced clean blocks, because the answer is classification every time.
Post
What made it work
What it cannot see without classification
Stopping leaked credentials
Microsoft ships the All Credential Types SIT, with checksums and patterns already built
Anything that is not a credential
Entra Internet Access inline DLP
A custom SIT for Contoso project references, imported before the policy was built, with a supporting keyword required within 300 characters for a High confidence match
A design document or roadmap that contains no project reference
Parts 4 and 5: MCP server blocking
Defender indicators block the destination outright
What the agent sends to an approved server
Part 6: Agent 365 governance
Approval, ownership and Conditional Access for agents
Which content an approved agent can ground on
The pattern is clear. Destination controls are binary: a server is allowed or it is not. Once a destination is approved, whether that is a sanctioned MCP server, Copilot or an external partner, the only thing that can stop the wrong content reaching it is a control that knows what the content is.
Why intellectual property is the hard case
Most DLP deployments start with personal and financial data because it is easy. A credit card number has a checksum. A PPSN has a fixed format. Microsoft ships hundreds of SITs for these, and a policy can be live in an afternoon.
Intellectual property has none of that. There is no built-in SIT for Contoso’s product roadmap, a formulation, a tender response or the code behind Contoso’s custom-developed pricing application. IP is defined by what a document is and who it belongs to, not by a pattern inside it. That makes it the case where classification matters most, and the one most organisations never get to.
Contoso’s crown jewels
Before choosing a classification method, list what actually needs protecting. For Contoso, whose flagship R&D programme – codename Project Halcyon – is the running example in this post:
IP asset
What it looks like
Best classification method
Project and product codes
CONTOSO-FIN-204815-K in specs, emails and chats
Custom SIT (regex and keywords)
Patent drafts and design specifications
Written on a standard Contoso template
Document fingerprinting
Custom-developed applications
The source code, scripts and configuration behind Contoso’s in-house apps, in any language
Pretrained Source Code classifier
Customer and supplier lists
Real names and account numbers from the CRM
Exact data match (EDM)
Strategy, M&A and roadmaps
Free-form documents and slide decks
Pretrained or custom trainable classifier, plus a manual label
Everything on the Engineering site
Whatever the team saves there
Default sensitivity label on the site library
No single method covers the list. That is the point of this post: IP protection is built from several classification methods layered together, then enforced by several types of DLP.
Key risks of losing Contoso’s intellectual property
Scenario
What could happen
Risk level
The departing engineer
Design files and the code of Contoso’s custom-developed apps copied to USB or a personal cloud account in the weeks before a resignation.
● Critical
Pasted into an AI app
A roadmap or specification pasted into a consumer AI tool to summarise it, where it may be retained or used for training.
● Critical
Sent to an AI agent’s tools
A coding agent passes the code of a custom-developed Contoso app to an approved MCP server, which logs it.
● High
Oversharing through Copilot
Copilot grounds an answer on an M&A document a user could technically open but should never have seen.
● High
External sharing
A patent draft emailed to an external partner before filing, or shared through an “anyone” link.
● Critical
Loss of trade secret status
Information only qualifies as a trade secret where reasonable steps were taken to keep it secret. Unclassified, unprotected IP weakens that position in any dispute.
● High
The last row deserves attention. Under the EU Trade Secrets Directive, transposed in Ireland by the European Union (Protection of Trade Secrets) Regulations 2018, information is protected only where its holder took reasonable steps to keep it secret. Classification and DLP are not legal advice, but they are evidence of exactly those steps. Discuss the specifics with your legal team.
Methods of classification
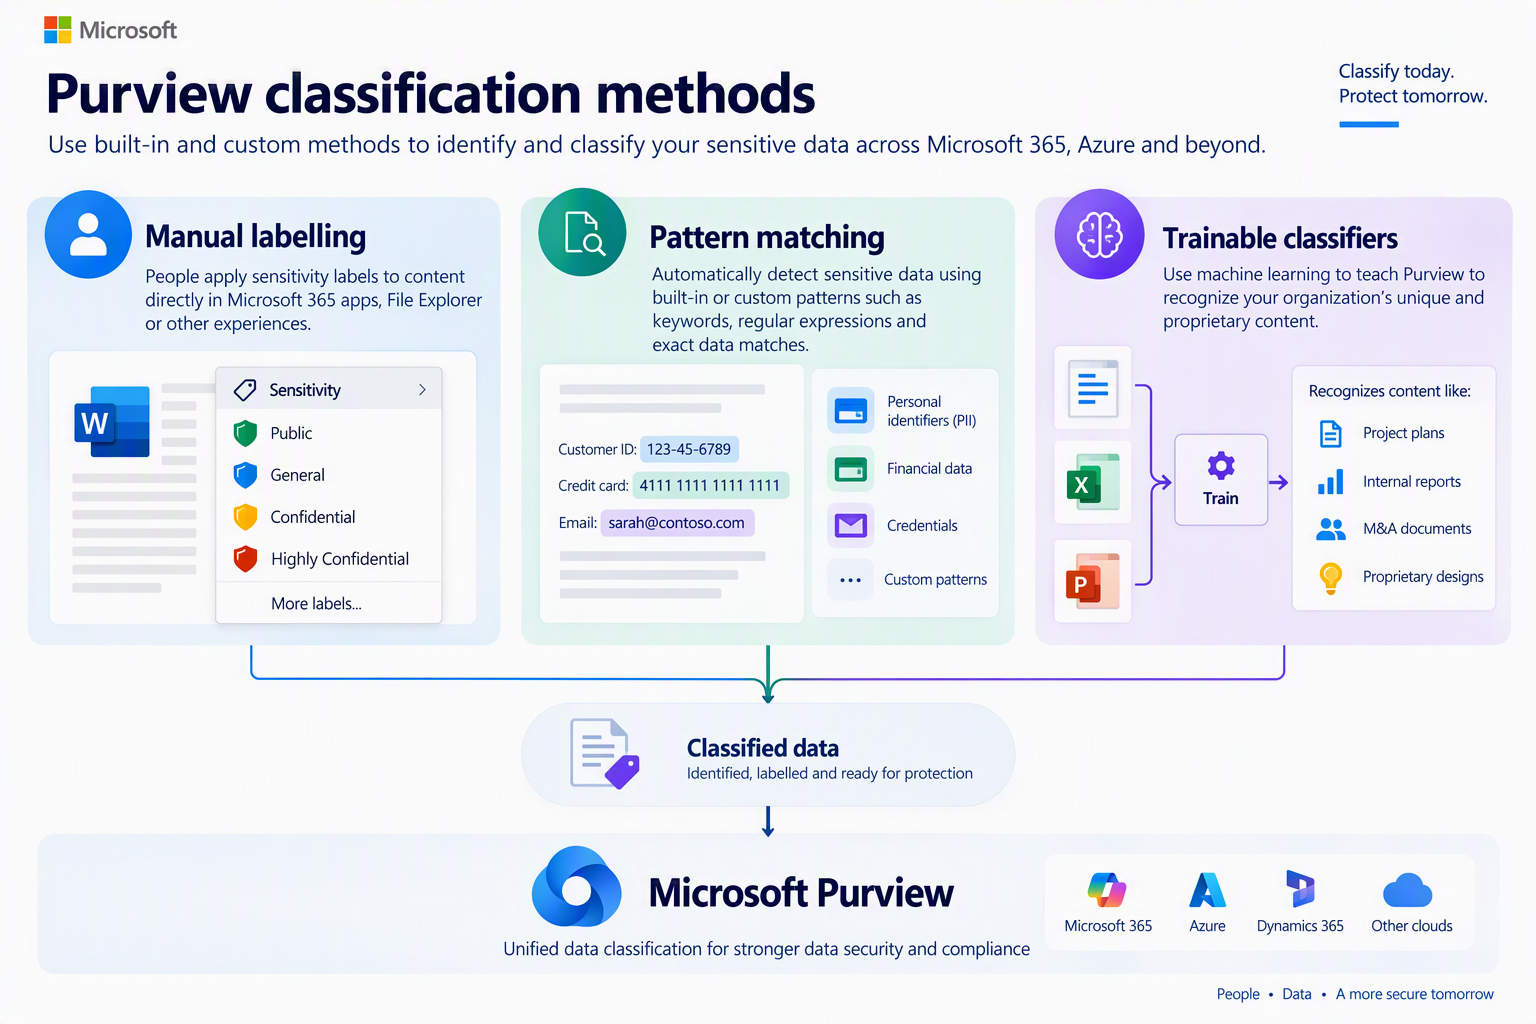
Microsoft Purview classifies content in three ways: manually, by automated pattern matching, and with trainable classifiers. In practice those break down into the methods below.
Method
How it decides
Strong for
Weak for
Manual sensitivity labels
The author decides
Strategy and M&A, where context matters
Consistency at scale
Default labels
Where the file is saved, or who created it
Engineering and R&D sites
Content that leaves that location
Built-in SITs
Microsoft patterns, checksums and keywords
Credentials, PII, financial data
Anything unique to Contoso
Custom SITs
Your own regex and keywords
Project codes, part numbers
IP with no identifier in it
Exact data match
Hashed values from your own source table
Customer lists, product catalogues
Unstructured documents
Document fingerprinting
Similarity to a standard template
Patent and design specification forms
Documents not written on the template
Pretrained classifiers
Machine learning on what the item is
Source code, IP, M&A, business plans
Precision; encrypted items
Custom trainable classifiers
Machine learning trained on your own samples
A document category only Contoso has
Non-English content; quick wins
Rule of thumb: if the IP carries an identifier, use a custom SIT. If it lives in a table, use EDM. If it is written on a standard template, use a fingerprint. If it is none of those, use a trainable classifier. And label anything only a person can judge.
One place to manage all of this.MC1486289 introduces a unified Classification Management experience in the Purview portal. It brings sensitive information types, Exact Data Match, trainable classifiers and document fingerprinting into one view, with search, filters and guidance in the creation flow on which method suits your scenario – the same decision the table above walks through. Public preview began in October 2026, with general availability scheduled from mid to late November 2026. Portal paths in this post may change as it rolls out.
Sensitivity labels: manual, default and automatic
A sensitivity label is the only classification that travels with the file. Every other method detects content each time it is evaluated; a label is written into the file’s metadata, stays with it wherever it goes, and can apply encryption that keeps working outside Contoso entirely.
Manual. The author chooses. Best where only a person can judge sensitivity, such as a board paper or an acquisition target.
Default. A label applied by policy or by a SharePoint document library. Everything saved to the Contoso R&D library is Highly Confidential – Contoso IP unless someone changes it.
Automatic. Client-side auto-labelling recommends or applies a label in the Office apps as a user works. Service-side auto-labelling applies labels to content already at rest in SharePoint, OneDrive and Exchange. Both use the SITs, fingerprints and classifiers described below as conditions.
Labels matter most once content is encrypted. Trainable classifiers only work on items that are not encrypted, so once a label encrypts a file, content-based detection can no longer read it. From that point on, the label is the only thing downstream controls can recognise, which is why label-based DLP conditions are not optional.
Sensitive information types
A SIT is a pattern, usually a regular expression, supported by keywords, checksums and a proximity window, with confidence levels for how much evidence was found. Microsoft ships several hundred. The credentials post used the bundled All Credential Types SIT, and it belongs in any IP policy too: source code and configuration files are where secrets hide.
For Contoso’s own identifiers you write a custom SIT. The project reference SIT used in the inline DLP post is a good model:
\bCONTOSO-[A-Z]{3}-\d{6}-[A-Z]\b
High confidence (85) – the pattern plus a keyword such as “project reference” or “confidential project” within 300 characters.
Medium confidence (75) – the pattern on its own.
The fixed CONTOSO- prefix means it cannot collide with any built-in type, and the next two sections explain why that matters. The New-ContosoSIT.ps1 script in the inline DLP repository builds and imports the rule package in one run, and takes -Prefix and -DisplayName parameters so it can be reused for any client.
A regex is not a SIT
regex101.com is the best place to build the pattern. Paste a candidate regex and a block of sample text and it highlights every match as you type, explains each token in plain English, and lets you keep a set of test strings that should and should not match. For Contoso, that is where you prove \bCONTOSO-[A-Z]{3}-\d{6}-[A-Z]\b matches CONTOSO-FIN-204815-K and rejects a five-digit number, a missing prefix or a reference glued to another word – before it goes anywhere near Purview.
What regex101 cannot tell you is everything else the pattern will match across Exchange, SharePoint, OneDrive and Teams. Purview’s regex engine is not one of regex101’s flavours either, so a pattern that works there still has to be proved in Purview. regex101 proves the pattern; it does not prove the SIT.
A loose pattern such as \d{6} or [A-Z]{3}-\d{6} will happily match phone numbers, dates, order numbers, postcodes and invoice references, and it will overlap with a large share of Microsoft’s built-in SITs, most of which are numeric identifiers. Deploy it in a blocking DLP rule and the service desk will know about it within the hour.
To see how many built-in SITs your tenant has for a new pattern to collide with, run:
What turns a regex into a usable SIT is the evidence around it:
A distinctive primary element. The fixed CONTOSO- prefix rules out almost every accidental match before anything else is checked.
Supporting keywords within a proximity window. “Project reference”, “codename” or “confidential project” within 300 characters is what lifts a match to High confidence. A string that merely looks like a reference stays at Medium.
Confidence levels in the policy. Block on High; use Medium for audit or a policy tip while you tune.
Testing against real content. The Test option on the SIT, fed with samples that should and should not match, is where false positives show up. regex101 proves the pattern; the Test option proves the SIT.
Inside the Contoso SIT: how proximity decides
A custom SIT is defined in an XML rule package and imported into Purview. This is the core of the Contoso Project Reference SIT used in the inline DLP post. Three parts of it do the work:
The regex is the primary element. Nothing is evaluated unless the text contains CONTOSO-, three letters, six digits and a check letter, bounded by word breaks. Purview matches it without regard to case.
The keywords are supporting evidence. On their own they match nothing. They only matter when they appear near a project reference, and matchStyle="word" means they must be whole words: “codename” counts, “codenames” does not.
The proximity window is 300 characters.patternsProximity="300" sets it: A keyword counts only if it falls within 300 characters of the reference. Inside the window, the match is High confidence (85). Outside it, or with no keyword at all, the match drops to Medium (75).
The DLP rule in the inline DLP post blocks at High confidence only. That one setting is what keeps false positives down: a reference has to look like a Contoso project code and be described as one before anything is blocked. A Medium match is still recorded, so it can drive an audit rule or a policy tip while you tune.
Here is how that plays out for prompts typed into an AI app, with the policy blocking at High confidence:
Prompt
SIT match
Blocked?
Why
“Summarise the risks on project reference CONTOSO-FIN-204815-K for the board”
High (85)
Yes
Pattern plus keyword in the same sentence
“Codename CONTOSO-RND-550731-H: draft a launch plan for this product”
High (85)
Yes
Pattern plus keyword
“Rewrite this update – Contoso project CONTOSO-OPS-118204-M is three weeks late”
High (85)
Yes
Pattern plus keyword
“Here is the spec for confidential project CONTOSO-ENG-904117-P. Find the weaknesses”
High (85)
Yes
Pattern plus keyword
“project code: contoso-hrs-300221-b – turn this into a job description”
High (85)
Yes
Case does not matter to the regex or the keywords
A pasted document with “Project ref” in the heading and CONTOSO-FIN-204815-K two paragraphs (under 300 characters) later
High (85)
Yes
Keyword inside the proximity window
“Is CONTOSO-FIN-204815-K a valid format for our tracker?”
Medium (75)
No – audit
Pattern with no supporting keyword
A long paste where “project reference” appears more than 300 characters from CONTOSO-FIN-204815-K
Medium (75)
No – audit
Keyword outside the proximity window
“Our codenames list starts with CONTOSO-RND-550731-H”
Medium (75)
No – audit
“codenames” is not the whole word “codename”
“Project reference CONTOSO-FN-204815-K”
None
No
Two letters, not three – the regex fails
“Project reference CONTOSO-FIN-20481-K”
None
No
Five digits, not six
“Project reference XCONTOSO-FIN-204815-K”
None
No
No word boundary before the prefix
“Project reference FABRIKAM-FIN-204815-K”
None
No
Wrong prefix
“What is our project code policy?”
None
No
A keyword on its own never matches
The last row is the important one. The keyword list contains everyday phrases that appear in thousands of emails and chats. On their own they do nothing; they only raise the confidence of a real project reference. That is the difference between a SIT and a keyword list, and it is why this SIT can block at High confidence without flooding the alert queue.
Prove it before you block. Paste these examples into a text file and run them through the Test option on the SIT. The results should match the table: six High, three Medium, five with no match. Purview lists a High match under Medium and Low as well, so seeing a value more than once is expected.
Custom SITs only find IP that carries an identifier. A design document that never mentions its project code passes straight through, which is why the next methods exist.
Exact data match
Exact data match (EDM) detects the actual values in your own data rather than a pattern that looks like them. You export a table, for example Contoso’s customer list with account numbers and contact names, hash it and upload the hashes. Purview then matches on those exact values, so a twelve-digit number only fires if it is a real Contoso customer account.
EDM gives the lowest false-positive rate of any method and suits structured IP: customer and supplier lists, a bill of materials, a product price book. The original data never leaves Contoso in clear text. The cost is operational: the source table has to be refreshed on a schedule as the data changes.
Document fingerprinting
Document fingerprinting is the most underused method for IP, and the best fit for any organisation that writes its IP on standard forms. You upload a blank template, such as Contoso’s patent disclosure form or design specification, and Purview converts its word pattern into a SIT. Any document written on that template then matches, whatever has been filled in.
Only a hash is stored; the original template cannot be reconstructed from it. Partial matching lets you set what percentage of the template text must be present for low, medium and high confidence, or select Exact to match only identical text.
Create it in the Purview portal under Information Protection > Classifiers > Sensitive info types > Create Fingerprint based SIT, or in Security & Compliance PowerShell:
$template = [System.IO.File]::ReadAllBytes('C:\Demo\Contoso-Design-Specification.docx')

New-DlpSensitiveInformationType -Name 'Contoso Design Specification' `
    -FileData $template `
    -ThresholdConfig @{ low = 40; medium = 60; high = 80 } `
    -IsExact $false `
    -Description 'Documents written on the Contoso design specification template'
Limits worth knowing before you promise it to anyone:
The template needs at least 256 characters of extracted text, and embedded documents in it are ignored.
It does not detect password-protected files, image-only files, files larger than 4 MB, or documents missing some of the template text.
Fingerprints share a 300 KB rule pack, which allows roughly 100 per tenant.
On devices, Advanced classification scanning and protection must be turned on in Endpoint DLP settings.
Trainable classifiers
Trainable classifiers identify an item by what it is rather than what it contains. For IP that is the only method that works on free-form documents with no identifiers and no template.
Pretrained classifiers are ready to use. Several map directly onto IP, including Source Code, Intellectual Property, Patents, Mergers and Acquisitions, and business and marketing plans. Check the current list in your tenant under Information Protection > Classifiers > Trainable classifiers, as it grows.
Custom trainable classifiers are trained on Contoso’s own documents. You provide a set of samples that definitely are the category, such as past tender responses, and a set that definitely are not. Purview trains on them, you review its predictions, and publish when the accuracy is acceptable.
Classifiers only work on items that are not encrypted.
Custom classifiers support English only.
Published custom classifiers cannot be retrained. To improve one, remove it and start again with larger sample sets.
The Source Code classifier fires when the bulk of the text is code, not on snippets pasted into a document or chat.
If you create a new SharePoint site for seed data, allow at least an hour for it to be indexed before training.
Precision versus coverage: EDM and exact fingerprints rarely misfire but only catch what they were built from. Classifiers catch far more but will produce false positives. Use the precise methods to block, and the broad ones to label, audit and warn while you tune.
The types of DLP
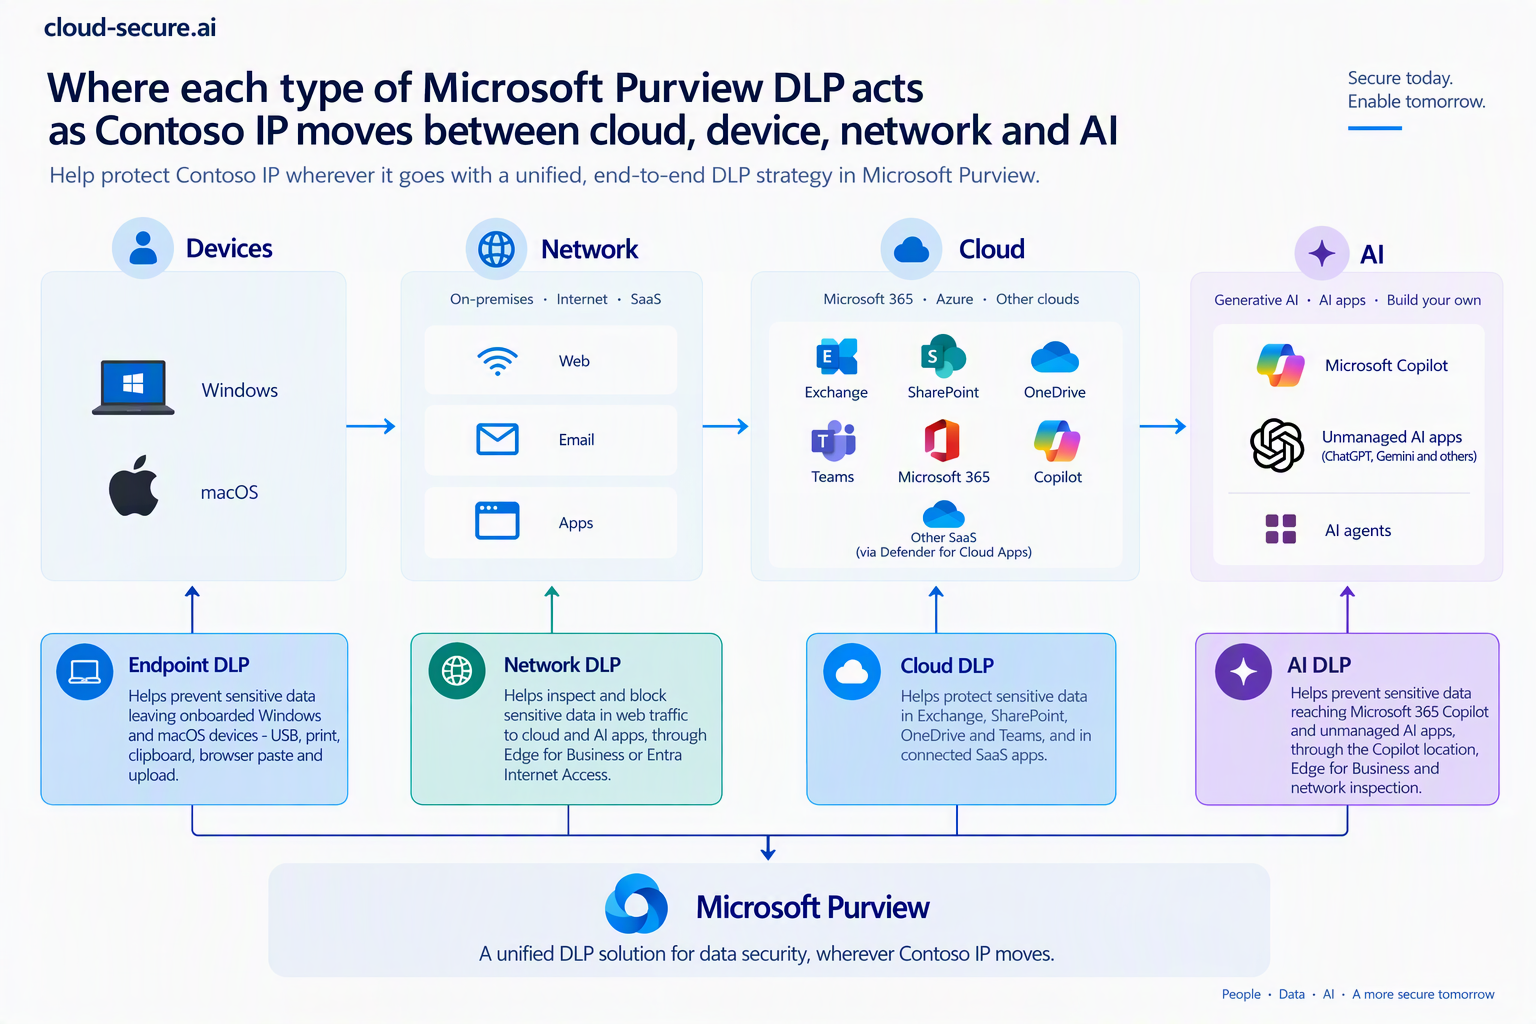
Classification decides what is sensitive. DLP decides what happens when that content moves. Purview DLP is not one control but a family, split into two policy scopes in the portal: Enterprise applications & devices and Inline web traffic. Each location sees a different part of the journey and offers different actions.
There are a lot of locations, and the table below lists them all for completeness. For the purposes of this post, the next sections focus on the route keeping most security teams awake: Contoso’s IP finding its way into generative AI.
Type of DLP
Where it acts
What it stops for Contoso IP
Microsoft 365 workloads
Exchange, SharePoint, OneDrive, Teams chat and channel messages
Patent drafts emailed externally, design files shared with guests or “anyone” links, project codes posted to external Teams chats
Endpoint DLP
Onboarded Windows and macOS devices
Copy to USB, print, upload to unallowed domains or personal cloud, copy to clipboard, access by unallowed apps – the departing engineer scenario
Microsoft 365 Copilot and Copilot Chat
Prompts, grounding content and agent interactions
Copilot processing labelled IP in its responses, and sensitive data typed into prompts
Inline web traffic – Edge for Business
Inside the managed browser
Pasting or uploading IP to unmanaged AI apps, with an in-page policy message
Inline web traffic – Network
Entra Internet Access, or a supported non-Microsoft SASE
IP sitting in sanctioned non-Microsoft cloud storage
On-premises repositories
File shares and SharePoint Server, through the Information Protection scanner
Legacy engineering shares nobody has migrated
Fabric and Power BI
Semantic models, lakehouses and warehouses
Pricing and product data uploaded to analytics workspaces
Protecting generative AI: where each type of DLP helps
AI reaches Contoso’s IP through several routes: a user pastes it into a prompt, uploads a file, asks Copilot a question that grounds on it, or lets an agent read it. No single DLP location covers all of them. Together they do:
Control
AI route it covers
What it does for Contoso IP
Microsoft 365 Copilot and Copilot Chat location
Copilot grounding, prompts and prebuilt agents in Copilot
Stops Copilot using content labelled Highly Confidential – Contoso IP in its responses, so a user who can open a file still cannot have Copilot summarise it
Endpoint DLP
Paste and upload into AI websites from managed devices, and desktop AI apps reading files
Blocks or warns on paste to browsers, upload to AI sites grouped as sensitive service domains, and access to labelled files by unallowed apps
Inline web traffic – Edge for Business
Typed and pasted prompts in Edge
Inspects the prompt in real time and blocks it before it leaves the browser, with a policy message the user can read
Inline web traffic – Network
Any browser, plus apps, APIs and add-ins, through Entra Internet Access or a supported SASE
Covers the browsers Edge for Business cannot – see the inline DLP post for tested results by app
Sensitivity labels with encryption
Any AI app, managed or not
Non-Microsoft AI apps cannot decrypt Purview-encrypted content, so a labelled file uploaded to them is unreadable
Exchange, SharePoint, OneDrive and Teams
AI-generated content shared onwards
A Copilot-drafted summary of Halcyon is still checked for SITs and labels when it is emailed or shared externally
Defender for Cloud Apps adds visibility of how Copilot is used and alerts on risky interactions, and DSPM for AI shows which AI apps are in use and what sensitive data reaches them. Neither blocks on its own; both tell you where to point the controls above.
Where Endpoint DLP protects
Endpoint DLP runs on Windows and macOS devices onboarded to Purview, and it is the control closest to the user. It acts on the actions people take with a file, wherever the file came from:
Activity
Contoso scenario it stops
Upload to cloud service domains
Design specification uploaded to a personal cloud drive or an AI website
Paste to supported browsers
Code from a custom-developed app pasted into a consumer AI chat
Copy to clipboard
Halcyon content copied out of a labelled document into an unmanaged app
Copy to removable USB device
The departing engineer’s copy of the project folder
Copy to network share
IP moved to an unmonitored file share before it leaves
Print
Patent drafts printed and walked out of the building
Transfer using Bluetooth
Files sent to a personal phone
Copy to remote desktop session
Data moved into a session on a machine Contoso does not manage
Access by unallowed apps
A labelled file opened by an unsanctioned desktop AI app or sync client
Each activity can be set to audit, block with override or block. Two settings matter for IP: Advanced classification scanning and protection must be on for fingerprint SITs to work on devices, and sensitive service domain groups let you treat AI websites differently from the rest of the internet.
Not every location understands every classifier
This is where classification and DLP design meet, and where most policies quietly fail. Locations support different conditions, and when you combine locations in one policy you keep only the conditions they all share.
Copilot acts on sensitivity labels for grounding content. Its location is only available in the Custom template and cannot be combined with any other location in the same policy. No label, no protection.
Fabric and Power BI support sensitivity labels and only a subset of SITs.
Inline web traffic classifies what it can parse. As the inline DLP post showed, a prompt sent in a binary format passes without a verdict, however good the classifier.
Encrypted content cannot be read by classifiers anywhere, so the label condition has to carry it.
The practical rule: build separate policies per location, and make sure every critical IP category is recognisable by a label as well as by content. Labels are the one classification every DLP location understands.
Where Global Secure Access prompt injection protection fits
Global Secure Access has a second AI control that is easy to confuse with inline DLP: prompt injection protection, configured as a prompt policy under Global Secure Access > Secure > Prompt policies and linked to the same security profile and Conditional Access policy as the content policy. It sits on the same TLS-inspected traffic path, but it answers a different question. Inline DLP asks is Contoso data leaving? Prompt injection protection asks is this prompt an attack on the model?
What it provides
What it does not provide
Blocks adversarial prompts and jailbreak attempts before they reach the model
Any recognition of Contoso IP. It has no SITs, labels, fingerprints or classifiers – a roadmap pasted politely passes straight through
Network-level enforcement with no change to the app, in any browser on a device running the Global Secure Access client
Inspection of files. It covers text prompts only
Preconfigured conversation schemes for ChatGPT, Claude, Cohere, DeepSeek, Gemini, Grok, Meta AI, Mistral, Perplexity, Pi and Qwen
Coverage of apps that do not send prompts as JSON, or of any app whose endpoint is missing from the conversation scheme
Custom schemes for in-house or other JSON-based AI apps, defined by endpoint URL and the JSON path to the prompt
Protection without TLS inspection, or for QUIC traffic. Untrusted certificates or QUIC left on means the prompt is never seen
A Block action. Allow with Always log lets you measure impact first, but blocks nothing
Inspection of prompts beyond 64,000 characters – longer prompts are truncated – and scanning is rate limited
Prompt activity recorded in the Generative AI Insights logs
Protection for local agents talking to their own tools or MCP servers – that is Defender AI agent runtime protection, covered in Parts 1 to 5
The two controls are complementary, not alternatives. Prompt injection protection stops someone attacking the model through Contoso’s network; inline DLP stops Contoso’s IP reaching the model in the first place. Only the second depends on classification, which is why this post exists. Deploy both on the same security profile, and do not present prompt injection protection to a customer as a data protection control.
Test each app yourself. Claude is in the preconfigured list, yet in the inline DLP lab Claude sent typed prompts as binary Protocol Buffers rather than JSON. Check the request content type in the traffic logs before claiming coverage for any app, exactly as the inline DLP validation method describes.
Data at rest versus data in motion: eDiscovery and DLP
DLP stops sensitive content moving from now on. It does not tidy up what is already there. The credentials post made the same point: the connection string emailed eight months ago is still sitting in a mailbox. Finding IP that is already at rest is a separate job, and the tools behave differently by workload.
Location
Finding it at rest (eDiscovery search)
Stopping it leaving (DLP)
Exchange Online
Searchable with SensitiveType, evaluated against the message body and indexed attachments when the item was indexed. A SIT created or changed later does not match older mail until it is reindexed. Images, scanned PDFs and partially indexed items are not evaluated
Evaluated as mail is sent and received. Exchange DLP is event-driven, not a scanner of mail already in the mailbox
SharePoint Online
Searchable with SensitiveType, including count and confidence ranges such as SensitiveType:"Credit Card Number|5..25"
Evaluates files at rest and when they are shared, and can restrict access to them
OneDrive
As SharePoint
As SharePoint
Teams chat and channel messages
Limited. Messages are stored in user and Teams mailboxes and evaluated on message text only, with lower accuracy for short messages. Files shared in Teams follow the SharePoint and OneDrive rules
Evaluated as messages are sent. Files shared in Teams are covered by the SharePoint and OneDrive locations
Microsoft 365 Groups
The group mailbox follows the Exchange rules; the group site follows the SharePoint rules
Covered through the Exchange, SharePoint and OneDrive locations
Two consequences matter for Contoso:
Create custom SITs early. A Contoso Project Reference SIT published today will not find project codes in mail indexed last year until those items are reindexed. Every week of delay is a week of email that a search will miss.
Search before you enforce. Run an eDiscovery search for the custom SIT, the fingerprint SITs and All Credential Types across all workloads first. It tells you how much IP is already exposed and gives the DLP policy a realistic baseline.
DLP is the opposite side of the same coin. It reads SITs, labels, fingerprints and classifiers in every location it covers – Exchange, SharePoint, OneDrive and Teams, plus devices, Copilot, inline web traffic, Defender for Cloud Apps instances, on-premises repositories and Fabric – and it is the only control that acts at the moment content leaves.
Putting it together for Contoso
Here is how everything above combines around one asset: Project Halcyon, Contoso’s flagship R&D programme.
Layer 1 – Classify
Component
Configuration
Label
Highly Confidential – Contoso IP, encrypting content and limiting access to the R&D group
Default label
Applied to the Project Halcyon SharePoint library
Custom SIT
Contoso Project Reference, at High confidence
Fingerprint SIT
Contoso Design Specification and Contoso Patent Disclosure templates
Classifiers
Pretrained Source Code (for Contoso’s custom-developed apps) and Patents
Auto-labelling
Client-side recommendation and service-side policy apply the label when any of the SITs or classifiers above match
Layer 2 – Enforce
Policy
Condition
Action
DLP-IP-M365
Label, project SIT or fingerprint SIT, shared outside Contoso
Block, with override and business justification for Legal
DLP-IP-Endpoint
Label, Source Code classifier or fingerprint SIT
Block USB, print and upload to personal cloud; audit clipboard
DLP-IP-Copilot
Highly Confidential – Contoso IP label
Prevent Copilot from processing content
DLP-IP-AIApps
Project SIT or Source Code classifier, to All unmanaged AI apps
The Defender and Agent 365 controls from the series sit on top: unsanctioned MCP servers blocked by indicators, agents approved before use, runtime protection inspecting what agents read, and GSA prompt injection protection blocking attacks on browser AI apps. They decide which doors exist; the first two layers decide what is allowed through them.
Now replay the risks. The departing engineer’s USB copy is blocked by Endpoint DLP because the files carry the label or match the Source Code classifier. The roadmap pasted into ChatGPT is blocked inline. Copilot will not ground answers on Halcyon documents. A patent draft emailed to a partner is stopped at Exchange. Every one of those outcomes depends on Layer 1.
Handling the alerts: the Triage Agent in DLP
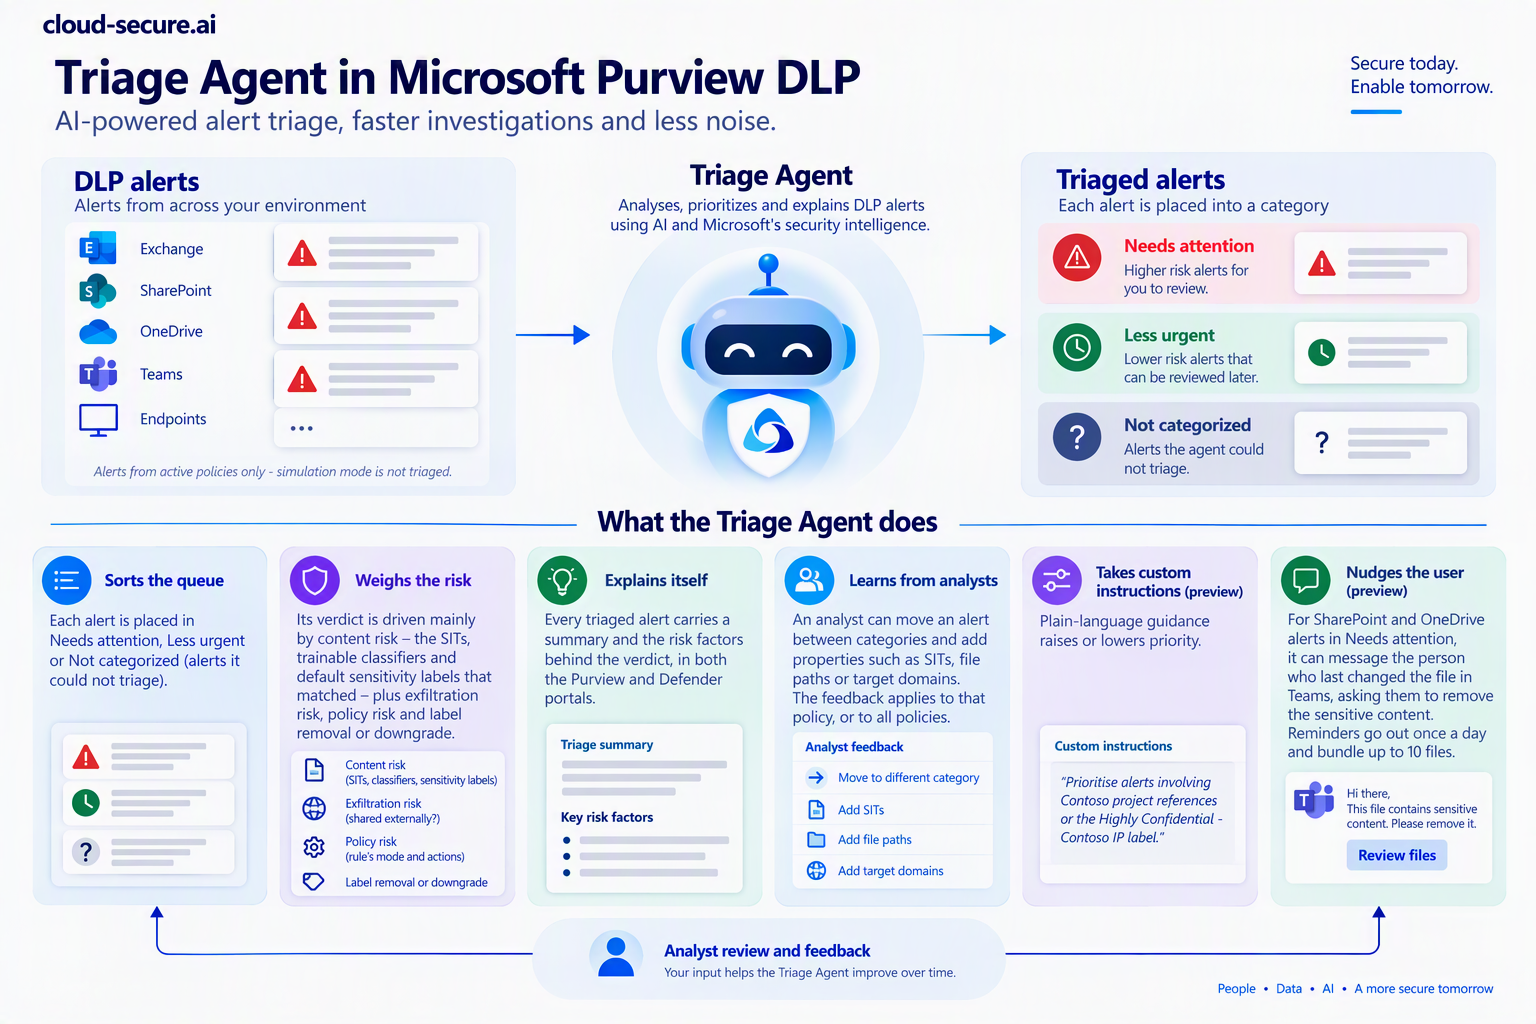
Layering classifiers has a cost: alerts. A Source Code classifier and a broad fingerprint will produce far more matches than a credential SIT, and a security team that cannot keep up with the queue will eventually stop reading it. The Triage Agent in DLP, a Security Copilot agent in the Purview portal, is Microsoft’s answer to that problem.
What it does
Sorts the queue. Each alert is placed in Needs attention, Less urgent or Not categorized (alerts it could not triage).
Weighs the risk. Its verdict is driven mainly by content risk – the SITs, trainable classifiers and default sensitivity labels that matched – plus exfiltration risk (was the data shared externally?), policy risk (the rule’s mode and actions) and label removal or downgrade.
Explains itself. Every triaged alert carries a summary and the risk factors behind the verdict, in both the Purview and Defender portals.
Learns from analysts. An analyst can move an alert between categories and add properties such as SITs, file paths or target domains. The feedback applies to that policy, or to all policies.
Takes custom instructions (preview). Plain-language guidance raises or lowers priority.
Nudges the user (preview). For SharePoint and OneDrive alerts in Needs attention, it can message the person who last changed the file in Teams, asking them to remove the sensitive content. Reminders go out once a day and bundle up to 10 files.
How it benefits Contoso
Halcyon alerts first. A custom instruction such as “Prioritise alerts involving Contoso Project Reference, the design specification fingerprint or the Highly Confidential – Contoso IP label” puts IP at the top of the queue, above the noise from built-in PII types.
Tuning without rewriting policies. When the Source Code classifier fires on a harmless script, analyst feedback teaches the agent to rank it lower, rather than someone weakening the rule.
Oversharing fixed at the source. The Teams reminder asks the engineer who left a design file in an open site to clean it up, without a ticket.
Evidence for the board. The Needs attention count is a cleaner measure of real IP risk than raw alert volume.
What to know before you switch it on
It only triages alerts from policies scoped to Exchange, Teams, OneDrive, SharePoint and devices. Alerts from the Copilot and inline web traffic policies – the AI routes above – are not triaged.
It ignores policies in simulation mode, so it adds nothing until a policy is turned on.
It analyses files up to 2 MB, and for alerts with 10 or more files it looks at the top 10 only. Device alerts need evidence collection for file activities turned on.
It looks back at most 30 days from the day it is enabled. Allow up to two hours for the first pass.
It runs on Security Copilot and consumes SCUs (Security Compute Units) in proportion to alert volume, so provision capacity and watch usage. It also needs Purview pay-as-you-go billing alongside per-seat DLP licensing.
Several capabilities are in preview. Confirm the current status in your tenant.
A practical sequence
Find what you have. Data explorer and Activity explorer show where existing SITs and labels already occur and how content moves, before any policy exists. DSPM shows the same through a risk lens, and an eDiscovery search for your custom SITs shows what is already sitting in mailboxes and sites.
Agree the crown jewels with the business. R&D, Legal and Product decide what counts as IP. Security cannot classify what nobody has defined.
Keep the label taxonomy short. Four or five labels people understand beat twelve they ignore.
Build classifiers per asset type, using the crown jewels table: custom SITs for identifiers, fingerprints for templates, EDM for structured lists, classifiers for the rest.
Test before you trust. Use the Test option on each SIT with samples that should and should not match, and check classifier predictions before publishing.
Auto-label in simulation first. Review what service-side auto-labelling would label before letting it apply encryption at scale.
Run DLP in simulation, then with policy tips, then block. Tips teach users what is sensitive; blocks without them generate tickets.
Switch on the Triage Agent once policies are live, with a custom instruction that puts Contoso IP first.
Review regularly. New projects need new codes, templates change, and classifiers drift as the business does.
Limits to know
Classification is never complete. Some IP will always be unlabelled and undetectable. Destination controls remain the backstop.
Encryption and detection pull in opposite directions. Encrypt too early and content classifiers go blind; rely on the label from that point.
Machine learning makes mistakes. Start classifier-based rules in audit or warn mode.
Licensing varies by method and location. Several capabilities in this post need E5, E5 Compliance or pay-as-you-go billing. Confirm against your own licence position before designing around them.
Features move quickly. Copilot and inline web traffic locations have changed repeatedly in 2026. Verify current behaviour in your tenant.
Wrapping up
Every control in this series is only as good as its ability to recognise what it is protecting. Destination controls decide where data can go; classification decides what the data is; DLP joins the two at every point data moves. For credentials and personal data Microsoft has done most of the classification work for you. For intellectual property, you have to do it yourself, with labels, custom SITs, fingerprints, EDM and classifiers layered together. Do that first, and every other control you have deployed starts to mean something.
Entra Internet Access, Defender for Cloud Apps and Purview: where the integrations actually stand
Prepared July 2026, updated 30 August 2026. Reflects product capability as at the date of writing and includes preview features, which are subject to change. Preview features should not be relied upon for compliance commitments.
There is a persistent assumption that Microsoft Entra Internet Access can simply consume the Sanctioned and Unsanctioned application tags maintained in Microsoft Defender for Cloud Apps, and that network-layer data loss prevention through Microsoft Purview is a finished, generally available capability. Neither is quite true today. This post sets out the two claims that matter most for anyone designing shadow IT enforcement on the Microsoft stack, using a worked example for Contoso (contoso.com), and then shows where each control plane sits in a high-level architecture. It also adds a third option that the debate over network DLP tends to obscure: make Edge for Business the only browser on managed Windows 11 devices through Intune, and let the browser enforce Purview policy inline – which is generally available now.
1. Entra Internet Access cannot integrate with Defender for Cloud Apps
There is no native integration between Defender for Cloud Apps application tags and Entra Internet Access. Entra Internet Access policies take web categories, FQDNs and URLs as destinations. They do not accept an app tag or a cloud app object, and Entra Internet Access is not one of the secure web gateways that Defender for Cloud Apps integrates with for automatic blocking.
In practical terms, there is no supported “unsanction it in Defender for Cloud Apps, block it in Entra Internet Access” pipeline today. The Defender for Endpoint path remains the only one-click enforcement route for the Unsanctioned tag: unsanctioned apps sync to Defender for Endpoint custom URL indicators automatically, enforced by Network Protection on the endpoint. That path is device-scoped and endpoint-dependent, and it cannot be scoped to an Entra security group.
Bridging the two is therefore customer-owned glue code: export the domains of unsanctioned apps from Defender for Cloud Apps and create matching FQDN rules in Entra Internet Access. This is automatable through Microsoft Graph, but it has to be re-run as tags and catalogue domains change. The one genuinely shared asset across both paths is the cloud app catalogue itself. Entra Internet Access consumes the same Defender for Cloud Apps catalogue for app identification and risk scoring, so risk scores stay consistent even though the enforcement binding does not exist.
One consequence worth flagging: Entra Internet Access is not a supported Cloud Discovery log source, so its Global Secure Access traffic logs do not populate the Discovered apps page in Defender for Cloud Apps. You get two discovery views – endpoint telemetry in Defender for Cloud Apps, and Application Usage Analytics in the Entra admin centre – and you correlate them yourself.
2. Scan with Purview via Entra Internet Access is still in preview – GA has slipped to September 2026
The Purview integration is real and productised. Entra Internet Access content policies can hand inspected content to Microsoft Purview, which evaluates sensitivity labels, sensitive information types, trainable classifiers and user risk, then returns an allow, audit or block decision that Global Secure Access enforces. Basic content policy is generally available. The Scan with Purview action at the Entra Internet Access (Global Secure Access) network layer, however, is still in public preview, and it is billed pay-as-you-go per request – it is not included in Microsoft 365 E5. This preview status is specific to the network enforcement point: the same Purview inspection delivered through Edge for Business is already generally available (see Process C), so “Scan with Purview is in preview” is only true of the Entra Internet Access integration, not of Purview inline protection in the browser.
The original Message Center notice (MC1181769) set general availability to begin mid-June 2026 and complete by mid-July 2026, following a public preview that ran from mid-November to mid-December 2025. That date did not hold. A 17 July 2026 update moved GA to September 2026, completing by the end of September, and a second notice (MC1419797, Roadmap ID 566528), which extends the same integration to text, prompts and AI interactions, has general availability beginning late September 2026 and completing by late October 2026. As at the end of August 2026 the Microsoft Learn documentation still carries the preview flag on the Scan with Purview action. Until GA lands, treat Scan with Purview at the network layer as a preview capability – pilot it in narrow scopes and audit mode, and do not build compliance commitments on it. What is generally available is the same Purview inspection delivered through Edge for Business, a different enforcement point for the same policy type; Process C below covers it, and it needs neither the Global Secure Access client nor the September 2026 GA date.
For anyone standing this up in preview, the prerequisites on the Global Secure Access side are specific: enable the internet access traffic profile with the correct user assignments, configure TLS inspection and a TLS inspection policy, create a file policy with a rule that specifies the Scan with Purview action, then bind those into a security profile linked to a Conditional Access policy. The global administrator must also activate Purview pay-as-you-go, though no charges apply during public preview. When it ships, the feature surfaces as a new Inline Web Traffic scenario in Purview DLP policy creation, able to detect and protect sensitive files sent to more than 35,000 unmanaged cloud applications, with matches, alerts and incidents managed centrally in Purview and Microsoft Defender.
The organisation in this worked example is Contoso (contoso.com). Contoso’s requirement is specific: protect data that has been classified as sensitive, and keep that protection in force when users interact with SaaS applications – including generative AI, cloud storage and content-sharing services reached through a browser. That splits into three enforcement planes that have to work together. The device plane stops sensitive files leaving a managed Contoso endpoint through channels the network never sees. The network plane inspects and controls sensitive content as it is transmitted to SaaS, from any browser, once traffic is routed and inspectable. The browser plane inspects prompts and uploads inside Edge for Business before they leave the device, and becomes the primary control once Intune has made Edge the only browser on the estate. Classification is the common dependency: all three planes act on Purview sensitivity labels, sensitive information types and trainable classifiers, so “what counts as sensitive” is defined once for contoso.com and enforced in all three. The process flows below show each plane end to end.
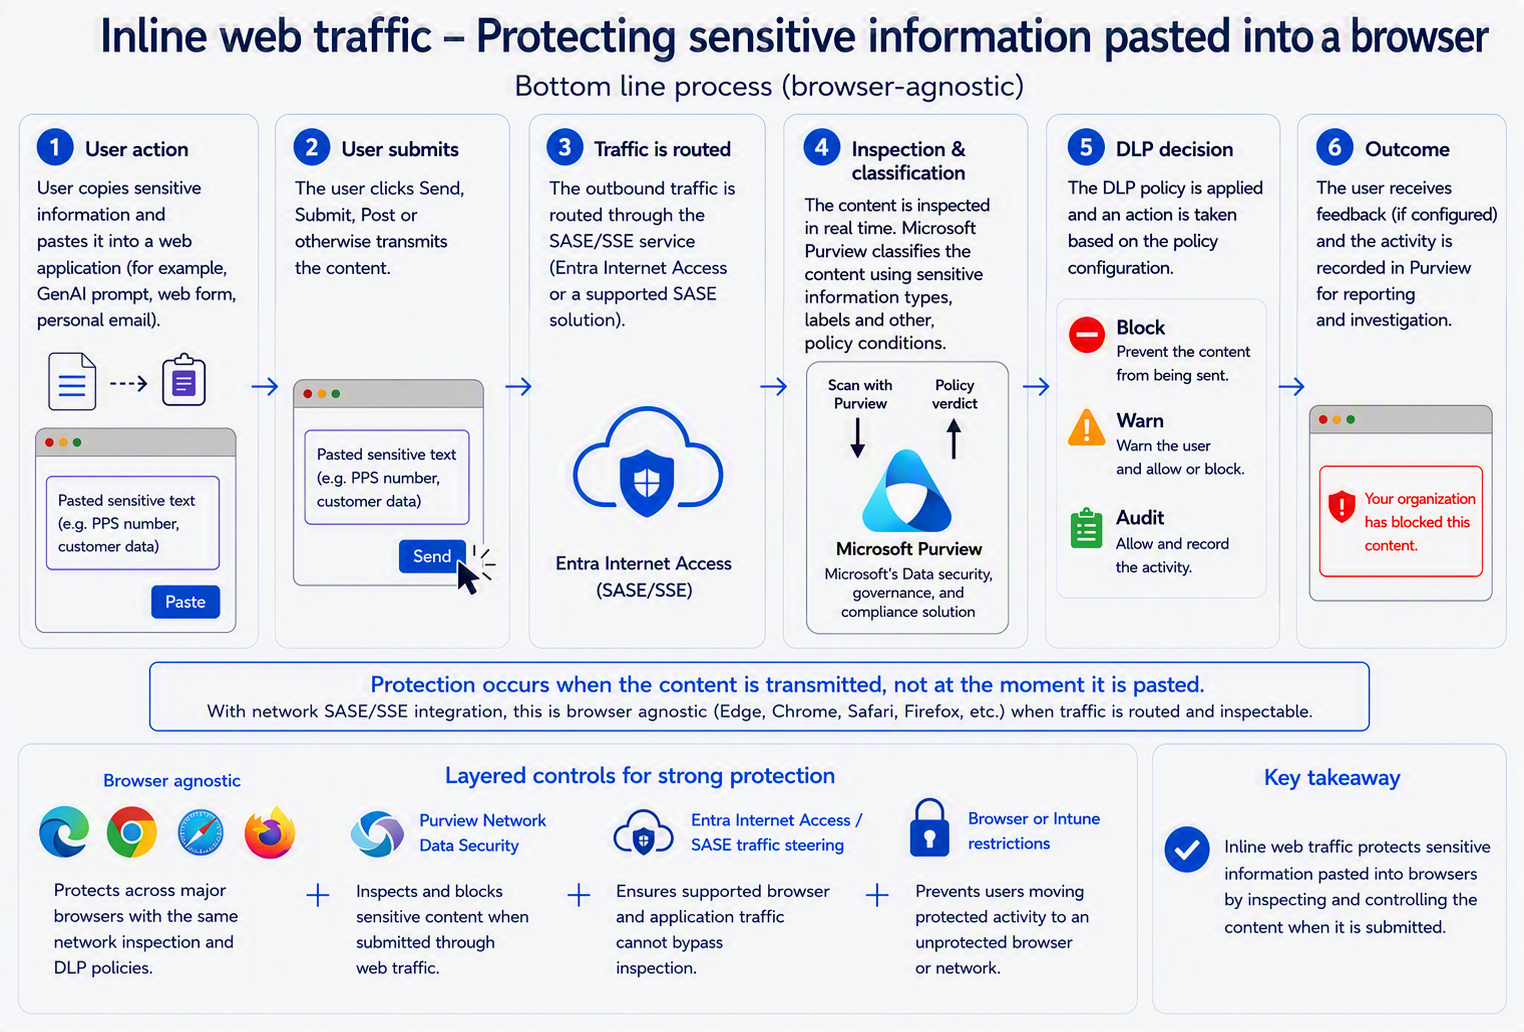
Process A – Inline web traffic (network plane): protecting sensitive content sent to SaaS
This is the path that meets the “protect the data when interacting with SaaS” half of the requirement. Protection occurs when content is transmitted, not at the moment it is pasted, and because enforcement is at the network layer it is browser-agnostic once traffic is routed through Entra Internet Access and inspectable.
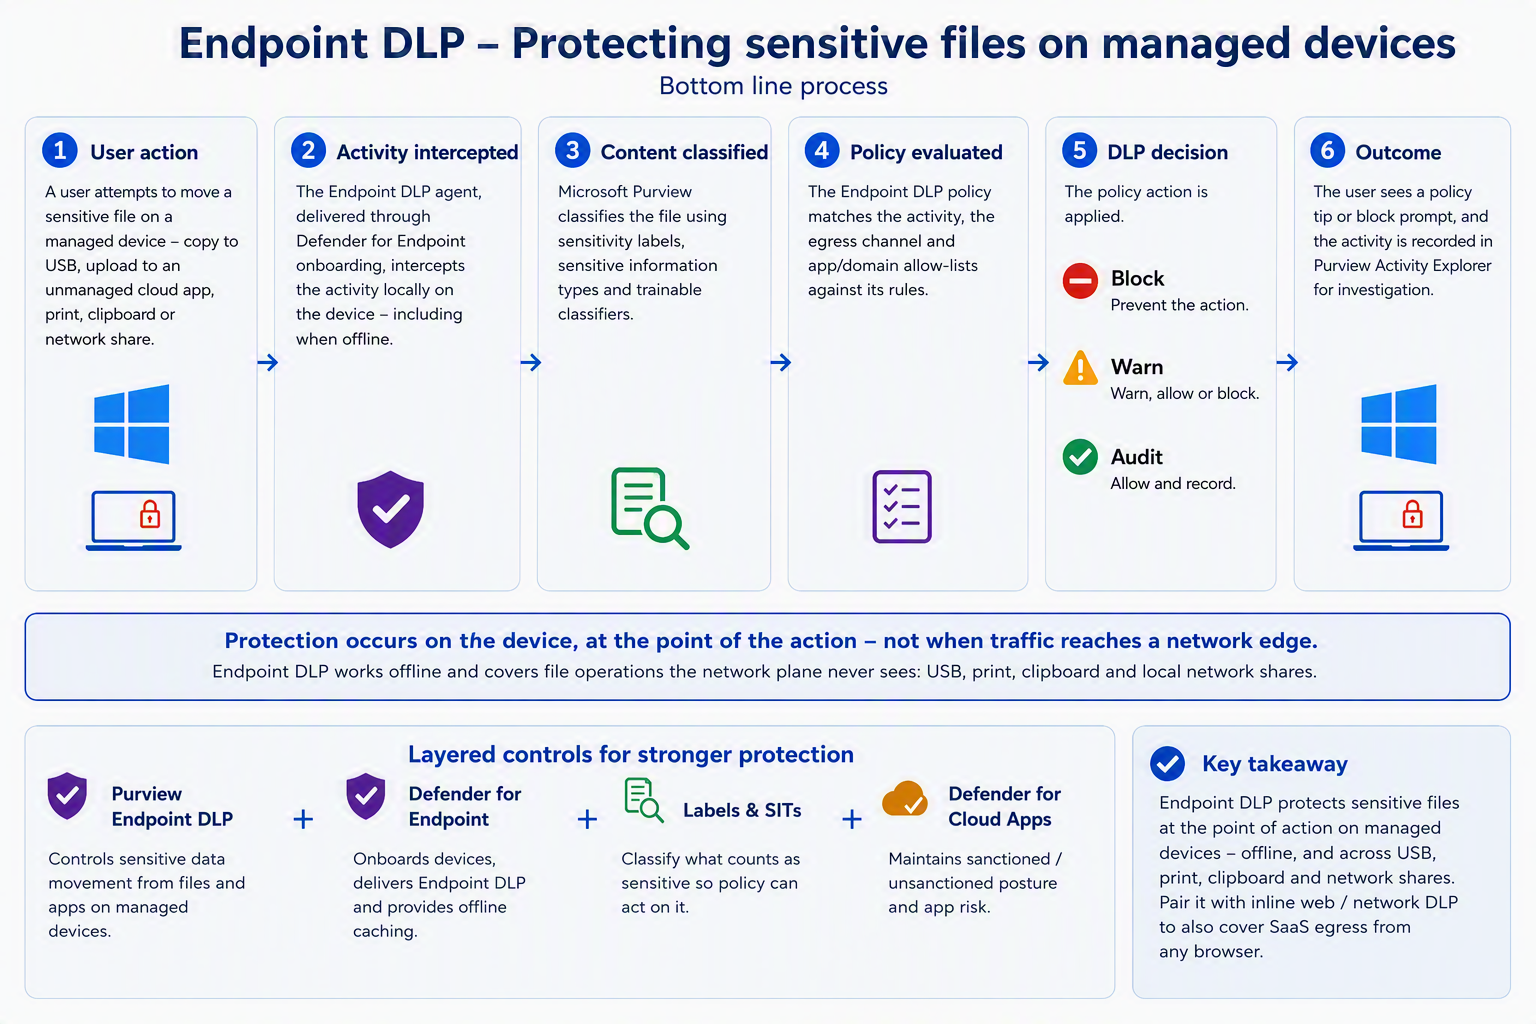
Process B – Endpoint DLP (device plane): protecting sensitive files on managed devices
This is the path that meets the “protect data classified as sensitive” half at the point of action on the device. Endpoint DLP enforces on the endpoint itself, works offline, and covers file operations the network plane never sees – USB, print, clipboard and local network shares – as well as uploads to unmanaged cloud apps and non-Edge browsers. It complements the network plane rather than replacing it.
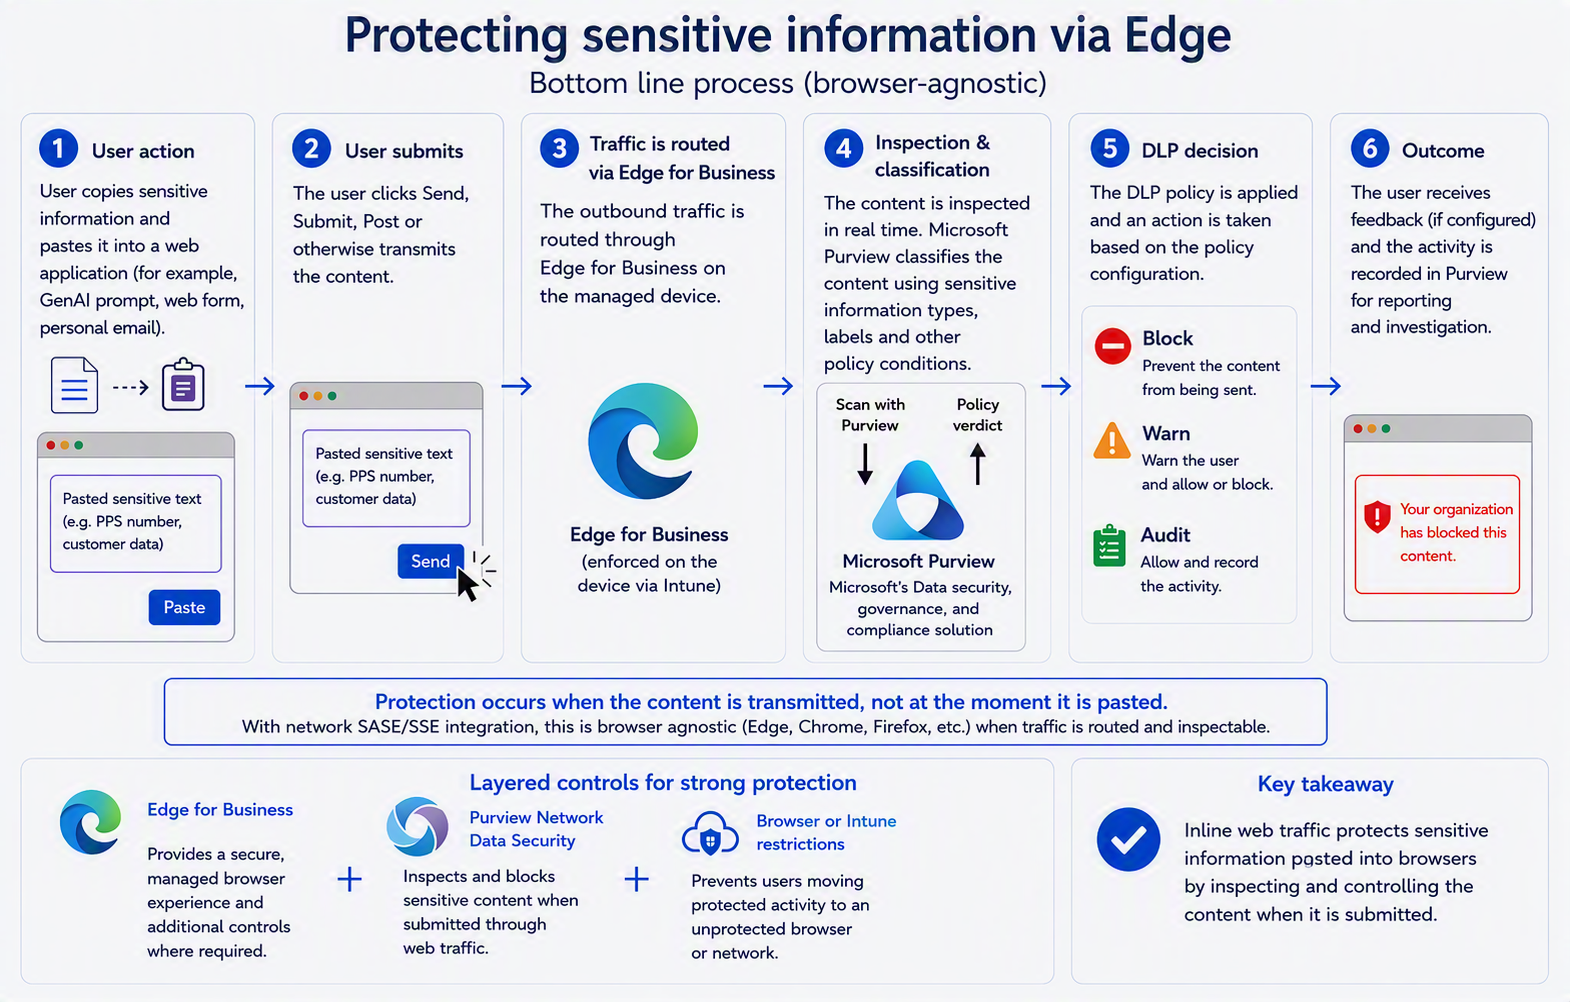
Process C – Browser plane: Edge for Business as the only browser on Windows 11, with Purview inline protection
There is a third enforcement plane for the data itself, and it is the one that is generally available today. If Contoso constrains its managed Windows 11 estate to a single browser, Microsoft Edge for Business becomes the enforcement point: the Purview DLP engine is built into the browser, so a prompt or a file upload is inspected before it leaves the device, with no Global Secure Access client, no TLS inspection and no dependency on the network-layer GA date. To be explicit, because it is the crux of this whole post: Scan with Purview via Edge for Business is generally available (GA), and it is only Scan with Purview via Entra Internet Access (the network-layer enforcement point) that remains in preview. The preview caveat in claim 2 does not apply here. Inline protection for unmanaged AI apps in Edge for Business reached general availability in November 2025 (Roadmap ID 486368, MC1046161), the automation that blocks unprotected browsers for users in scope followed in October 2025 (MC1151234), and inline protection of sensitive text moved onto the pay-as-you-go In Transit Protection meter from 31 October 2025 (MC1154787). It is worth being precise here, because the two capabilities are routinely conflated: this is not the network-layer Scan with Purview action from claim 2. It is the same Purview Inline web traffic policy type with a different enforcement point, and it is the browser rather than the Global Secure Access edge that does the inspecting.
Edge-only is an Intune design decision, not a Purview setting. On a Windows 11 device that is Entra joined and Intune managed, four controls make it stick:
Application control. An App Control for Business policy (Intune > Endpoint security > App Control for Business) is the durable control. Build the base policy from the built-in controls – trust Windows components and Store apps, and trust apps from the managed installer so that the Intune Management Extension stays the sanctioned install path – then add a supplemental policy carrying explicit deny rules for the third-party browser publishers (Google LLC, Mozilla Corporation, Brave Software, Opera and Vivaldi). An explicit deny wins over any allow, and publisher rules catch the per-user installs that Chrome and Firefox drop into %LocalAppData% without administrator rights. Extend the deny rules to the packaged (MSIX) versions in the Microsoft Store as well, or block the Store, because the trust-Store-apps option in the base policy can otherwise let a Store-installed Firefox through. Deploy in audit mode first and read the CodeIntegrity events before enforcing. AppLocker over a custom OMA-URI still works and scopes per user or group, but Microsoft are no longer adding features to it, so treat it as the fallback rather than the design.
Clean-up and defaults. Remove browsers already present with Intune Win32 uninstall assignments or a remediation script, and set Edge as the default handler for http, https, .htm and .html through a DefaultAssociationsConfiguration XML delivered from Intune, so links from Outlook, Teams and Office open in Edge without prompting. Keep users as standard users – LAPS for the local administrator account, Endpoint Privilege Management for the exceptions – because none of this holds for a local administrator.
Edge identity and version. Edge policies in the Settings Catalog force browser sign-in, restrict sign-in to the contoso.com tenant, disable guest mode and keep Edge on a current stable channel: inline protection needs one of the two latest stable versions, from version 144. Policies for unmanaged apps apply across every Edge profile on a managed device, including InPrivate; policies for Entra-connected apps apply only in the work profile, which is why the work profile has to be enforced rather than encouraged.
The Microsoft-managed shortcut. The Edge management service (Microsoft 365 admin centre > Settings > Microsoft Edge > Security settings) has a Block other browsers switch that creates the Intune configuration policy for you; it needs an Intune licence, and it takes precedence over every other setting in that profile. Purview does the same thing automatically for users in scope of a block policy: two security groups, two Edge configuration policies and two Intune policies appear, Firefox and other browsers are blocked outright, and Chrome is blocked unless the Purview extension for Chrome is installed and current, in which case Chrome runs with the AI app list denied. That automation is scoped to the DLP policy, so it is not a substitute for a standing Edge-only baseline, but it is a useful signal that Microsoft themselves treat the other browsers as the bypass to close.
On the Purview side the policy is the same Inline web traffic scenario the network plane uses, with a different enforcement point that is generally available. Create it under Data loss prevention > Policies > Create policy > Inline web traffic, scope the cloud apps through Adaptive app scopes > All unmanaged AI apps, and on Choose where to enforce the policy select Edge for Business (the GA path) rather than Network and non-Microsoft secure browsers (which routes to the preview network integration). The rule actions are Restrict browser and network activities > Text sent to or shared with cloud or AI apps, and File uploaded to or shared with cloud or AI apps, each set to audit or block; Adaptive Protection can be used as a condition so that the action varies with user risk. Saving the first policy triggers the Edge management service automation described above, which needs an admin holding Directory Reader, Microsoft Edge administration and Intune administration, and does not support tenants using Intune multi-admin approval. Run it in simulation mode first, then read Activity Explorer with the enforcement plane filtered to browser.
Three limits keep this from replacing Process A. First, scope: inline protection for unmanaged apps applies only to the Purview catalogue of supported unmanaged apps – a curated list of consumer generative AI services (ChatGPT, Google Gemini, DeepSeek, Grok, Meta AI, Perplexity, the consumer version of Copilot and around a dozen more) – not the tens of thousands of unmanaged cloud apps the network path targets. Entra-connected SaaS is covered separately through Defender for Cloud Apps in-browser protection, where session policies are enforced natively in Edge and Enforce usage of Edge for Business can be set to Allow access only from Edge. Second, egress the browser never sees – desktop applications, APIs, add-ins and sync clients – stays a network-plane or device-plane problem. Third, billing: unmanaged-app inline protection in Edge is a pay-as-you-go capability on the In Transit Protection meter, just as Scan with Purview is; only the Entra-connected app scenarios are included in Microsoft 365 E5. Two interactions with the other planes also need to be designed in. Endpoint DLP takes precedence over the inline Edge policy where both target the same user, context and action, so if Process B already blocks uploads to the same apps the Edge policy will silently do nothing. And with Edge as the only browser, Defender for Endpoint web protection is enforced natively by SmartScreen, Network Protection’s job narrows to non-browser processes, and the Purview extensions for Chrome and Firefox drop out of scope entirely.
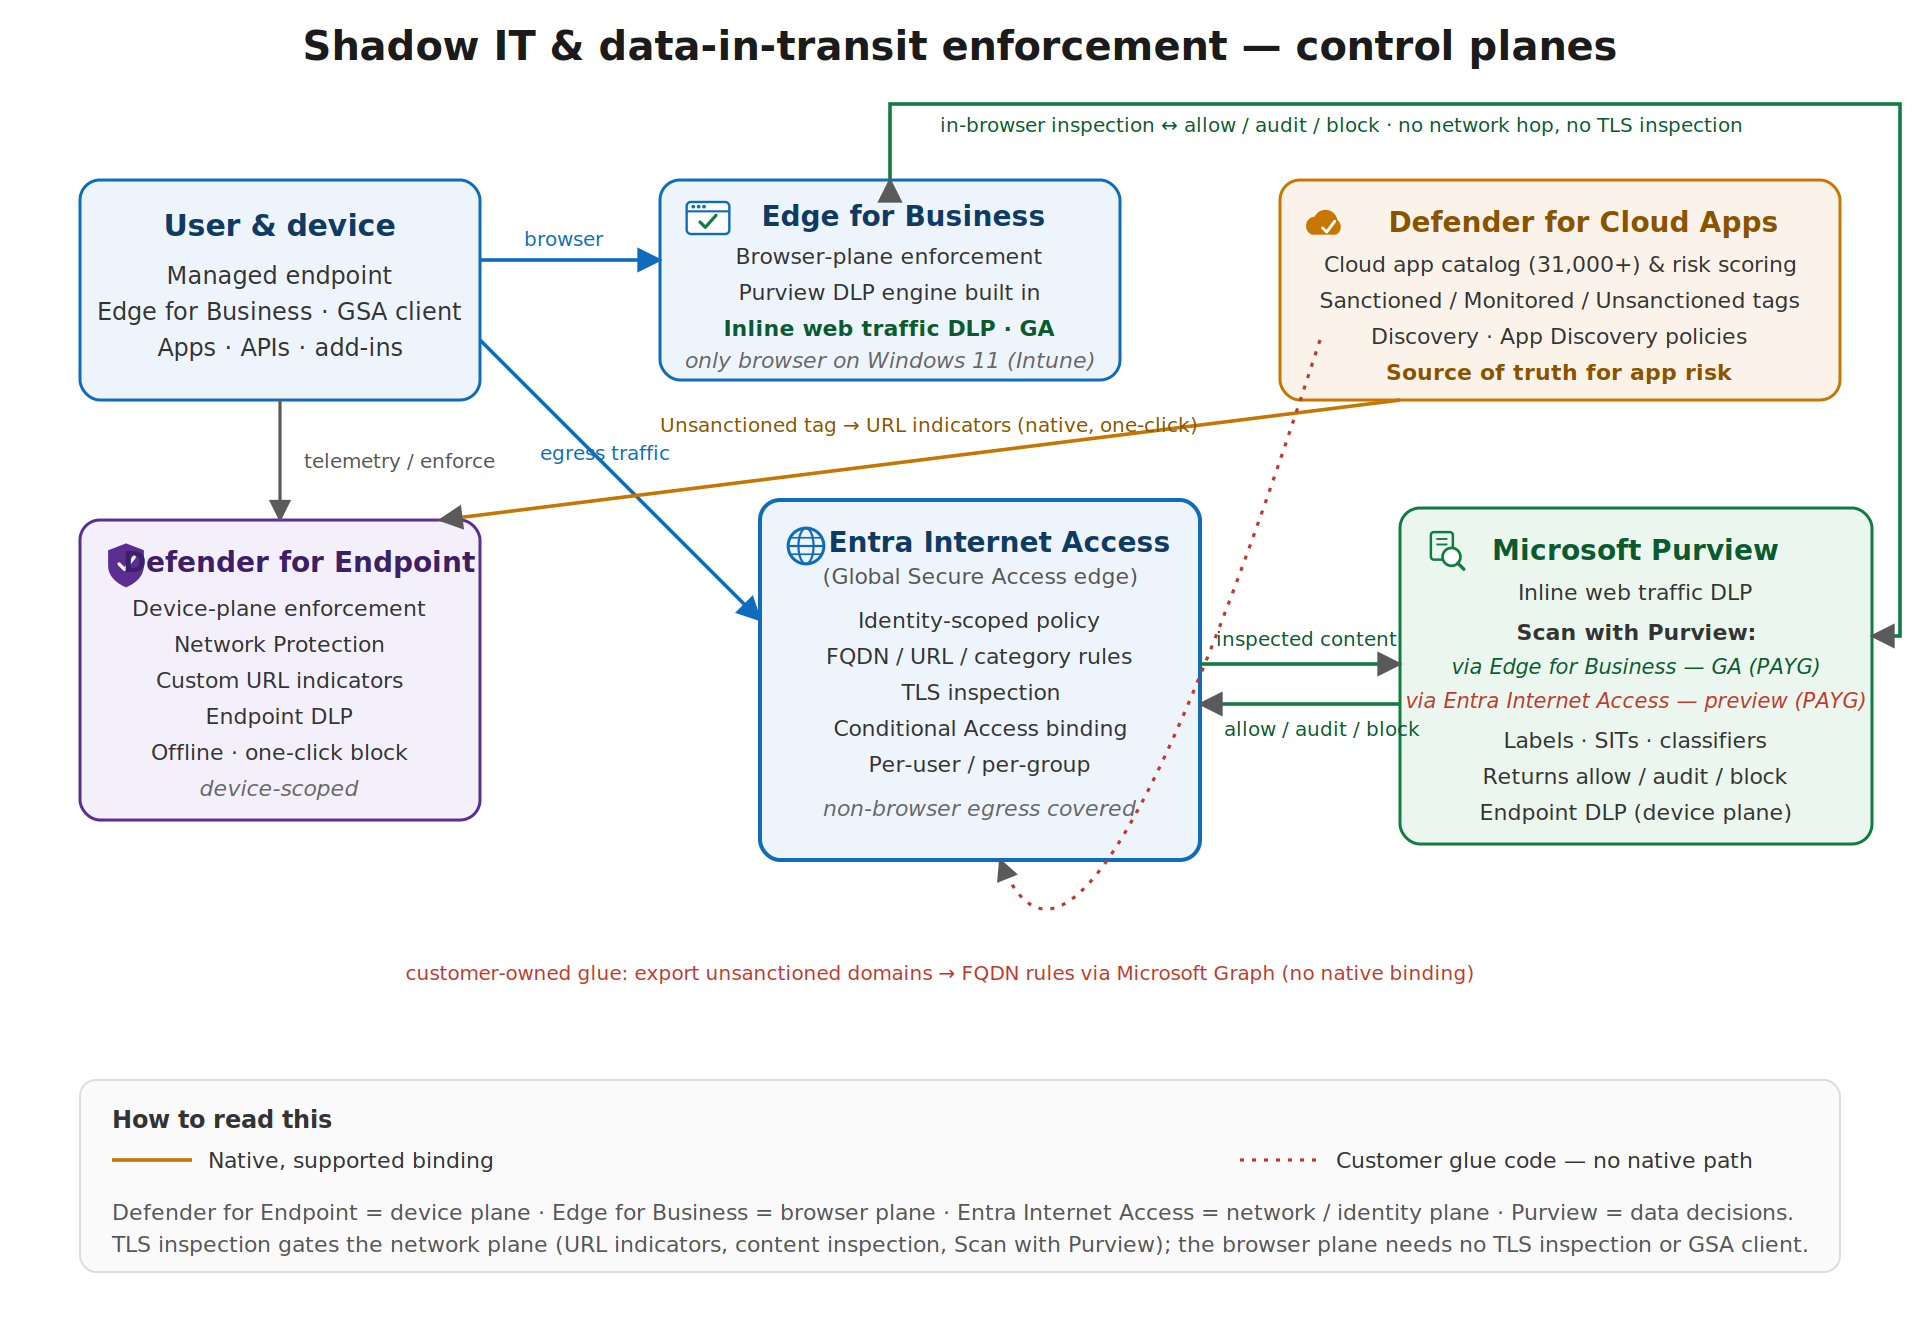
High-level architecture
The four control planes are complementary, not alternatives. Defender for Cloud Apps discovers, scores and holds the sanctioned/monitored/unsanctioned posture; Defender for Endpoint enforces on the device plane and offline; Edge for Business enforces Purview policy inline in the browser on managed Windows 11 devices where Intune has made it the only browser; Entra Internet Access enforces identity-scoped policy at the network edge and is the delivery point for Purview network DLP. The diagram below shows how traffic and signals move between them.
Three design points fall straight out of that picture. First, TLS inspection is the enabling dependency, not an optional enhancement – URL-level threat indicators, content inspection and the Purview integration all depend on it being deployed, with the certificate distributed through Intune. Second, the endpoint and network planes can contradict each other: Defender for Endpoint evaluates its web protection in a fixed order and allow indicators take precedence over web content filtering, so an app sanctioned in Defender for Cloud Apps can remain reachable even where a category block exists. Where both planes are active, document which plane owns which decision and avoid encoding the same intent twice. Third, the browser plane and the device plane overlap: Endpoint DLP takes precedence over the inline Edge policy for the same user, context and action, so an Edge for Business policy can pass testing and do nothing in production if Process B already covers the app. Decide which plane owns prompts and uploads to the AI apps, and keep the other in audit.
Recommended target pattern
Discover and score in Defender for Cloud Apps. Keep the cloud app catalogue and App Discovery policies as the single source of truth for application risk.
Enforce the organisation-wide baseline through Defender for Endpoint. Accept the up-to-three-hour propagation and the device-group scoping model for blanket blocks and warn-and-educate.
Make Edge for Business the only browser on managed Windows 11, and enforce inline. App Control for Business deny rules for the other browsers, Edge as default, work profile enforced, then an Inline web traffic DLP policy with Edge for Business as the enforcement point for the supported unmanaged AI apps. This is generally available now and is the fastest route to blocking sensitive prompts to consumer AI.
Deliver exceptions and identity-scoped policy through Entra Internet Access. Use security profiles linked to Conditional Access for per-group allow lists, risk-based restriction and non-browser egress.
Layer Purview network DLP for data in transit – once it reaches GA, currently September to October 2026 – for the long tail of unmanaged apps and the non-browser egress that the browser plane cannot see. Start narrow: unmanaged AI apps and highest-sensitivity labels, in audit mode, before moving to block.
Automate the tag-to-rule bridge. Build a scheduled Graph-based job that exports unsanctioned app domains and reconciles them against Entra Internet Access FQDN rules for contoso.com, until Microsoft close this gap natively.
Global Secure Access is developing rapidly. Several capabilities described here, including the Scan with Purview action and text and prompt inspection, are in preview and subject to change. Validate licensing entitlements against your current agreement before finalising design decisions.
Bridging the gap: letting Defender for Cloud Apps and Entra Internet Access co-exist
The architecture above is honest about one thing: there is no native binding between the Defender for Cloud Apps Unsanctioned tag and Entra Internet Access. That does not mean Contoso has to choose one or the other. The two planes answer different questions – which applications may be reached at all (Defender for Cloud Apps, through its catalogue, risk scoring and app tags) and which identities may reach a given destination, under what conditions, with what inspection (Entra Internet Access, at the network edge). Run together, Defender for Cloud Apps supplies the granular, catalogue-driven shadow IT control that Contoso is already paying for in its Microsoft 365 subscription, while Entra Internet Access – in my view the stronger web filtering service of the two, with real identity-scoped policy and Conditional Access binding rather than device-scoped indicators – owns the web-filtering and secure web gateway role. The bridge is three settings, and it is deliberately not a shared policy object: it is a division of labour that keeps each plane doing what it does best.
1. Put Defender for Endpoint network protection into block mode
Network protection is the enforcement muscle behind the Defender for Cloud Apps integration, and it only enforces when it is in block mode. In audit mode the indicators are evaluated and logged but nothing is stopped, and when it is disabled the Unsanctioned tags are, in the phrase one practitioner uses, just stickers in the portal. Deploy it through Intune (Endpoint security > Attack surface reduction, or the Settings Catalog) and confirm the state on a device with Get-MpPreference | Select-Object EnableNetworkProtection – the value must be 1 (block), not 0 (disabled) or 2 (audit). Two operational notes matter here: network protection blocks at the domain level, not full URL paths, and it cannot inspect QUIC, so disable UDP 443 in the managed browsers or with a Windows Firewall rule to stop non-Edge browsers slipping past the block over QUIC.
2. Enable custom network indicators – but leave MDE web content filtering off
This is the part that lets the two services share a device without fighting over it. In Microsoft Defender XDR, under Settings > Endpoints > Advanced features, turn on Custom network indicators, and in Settings > Cloud Apps > Cloud Discovery > Microsoft Defender for Endpoint, turn on Enforce app access. That is the whole dependency. Defender for Endpoint does not need its own web content filtering switched on: web content filtering is MDE’s category-based blocking, and it is a separate feature from the custom URL/IP indicators that the integration uses. With custom network indicators enabled, network protection simply reads the block (and warn) indicators that Defender for Cloud Apps populates when an app is tagged Unsanctioned (or Monitored), and enforces them on the endpoint. Contoso therefore gets Defender for Cloud Apps app governance without turning on a second, overlapping web-filtering engine on the device – the category-level web filtering stays with Entra Internet Access, where it belongs. This is also why the planes do not collide: Defender for Cloud Apps writes indicators, network protection enforces them at the domain level, and Entra Internet Access continues to enforce identity-scoped category, FQDN and URL policy at the edge with TLS inspection. The one precedence rule to keep in mind is Defender for Endpoint’s own order for indicators – Allow > Warn > Block – so an explicit allow indicator will override a category block. Defender for Cloud Apps never auto-creates allow indicators for sanctioned apps, so left alone the two planes reinforce rather than cancel each other; just avoid hand-authoring allow indicators for anything you also filter by category at the edge.
3. Create an app discovery policy that unsanctions new risky apps automatically
The final piece makes the baseline self-maintaining. Rather than tagging apps by hand, create an app discovery policy (Cloud Apps > Policies > Policy management > Create policy > App discovery policy) built from the New risky app template. Under App matching all of the following, set the Risk score filter to the risky band and add an App tag filter of does not equal Sanctioned so the policy can never turn on Contoso’s approved apps. Under Governance, select Tag app as unsanctioned. From then on, any newly discovered application whose risk score falls in that band is unsanctioned automatically, its domains sync to Defender for Endpoint as block indicators, and network protection blocks it within the integration’s roughly three-hour SLA.
One point worth stating plainly, because the slider is a frequent source of error: in Defender for Cloud Apps a lower score is the riskier one. The catalogue scores each app from 0 to 10, where 0 is the highest risk and 10 the lowest, so Contoso’s intent – unsanction anything risky – is expressed as a risk score of 0 to 4. Setting the filter to that range, with Sanctioned apps excluded and the daily-traffic threshold left generous to cut noise, gives a durable rule: the safe, high-scoring apps (5 and above) are left alone, the genuinely risky new arrivals are blocked on the device automatically, and anything Contoso wants to permit as an exception is still delivered cleanly through an identity-scoped Entra Internet Access allow, not through hand-edited endpoint indicators.
What this buys Contoso
The net effect is that Contoso takes full advantage of the Microsoft 365 subscription it already holds. Defender for Cloud Apps does the discovery, risk scoring and automated shadow IT governance – the granular control – and pushes its verdicts to the endpoint through network protection without needing MDE’s own web filtering turned on. Entra Internet Access remains the web filtering and secure web gateway of record, delivering per-user and per-group policy, category filtering, TLS inspection and the delivery point for Purview network DLP when Scan with Purview reaches GA. Neither service is subordinated to the other: they co-exist, each owning the decisions it is best placed to make, and the only ongoing task is the tag-to-rule bridge noted in the target pattern – reconciling the domains of newly unsanctioned apps into Entra Internet Access FQDN rules through Microsoft Graph, until Microsoft close that gap natively.
A note on Scan with Purview costs: they are very small
Because Scan with Purview and the inline protection scenarios are billed pay-as-you-go rather than bundled into Microsoft 365 E5, the natural question is what that actually costs. In practice the answer, for a normally-behaving user base, is: very little. The network and browser inline scenarios are metered on Microsoft Purview’s In Transit Protection meter, charged per request against traffic that DLP actually inspects – not per user, per device or per policy. You pay for what is scanned, so the bill scales with the volume of sensitive-content submissions to the destinations you have chosen to protect, not with headcount.
Two design choices keep that volume, and therefore the cost, low. First, scope narrowly: point the content policy at the specific FQDNs and unmanaged AI destinations that matter (the worked examples target ChatGPT and Gmail upload endpoints, not the whole web), so the meter only ever sees a small slice of egress. Second, classification happens before metering in the sense that matters operationally – you are protecting a handful of high-sensitivity labels and sensitive information types, not every byte a user transmits. For most Contoso-sized estates the monthly In Transit Protection charge lands in the low tens of euro rather than anything that would trouble a security budget, which is why the recommended pattern is to pilot it in audit mode without hesitation on cost grounds and only widen scope deliberately.
Two caveats worth stating so the number is not a surprise. Pay-as-you-go billing must be enabled, with an Azure subscription linked to Purview, before the network-enforcement option even appears in the DLP wizard; and you should confirm current per-request pricing against your own tenant, since the meter rate can change and varies by region. Model it for real numbers in the Azure Pricing Calculator, and watch consumption in the Purview Usage center once live. For the billing model and the request definitions, see Learn about Microsoft Purview billing models; to estimate your own figure, use the Azure Pricing Calculator.